










By Global Tech & Retail Desk
Published: October 2023
Main Facts: The Evolving Anatomy of E-Commerce Traffic
For over two decades, the term "bot" was universally associated with digital maliciousness. E-commerce security teams and cybersecurity specialists spent countless resources defending their digital storehouses against automated scrapers, inventory scalpers, and credential-stuffing cybercriminals. These bad actors sought to siphon proprietary product pricing data, lock down high-demand holiday merchandise for resale, or brute-force consumer accounts using stolen credentials.
Today, that black-and-white threat model has entirely fractured.
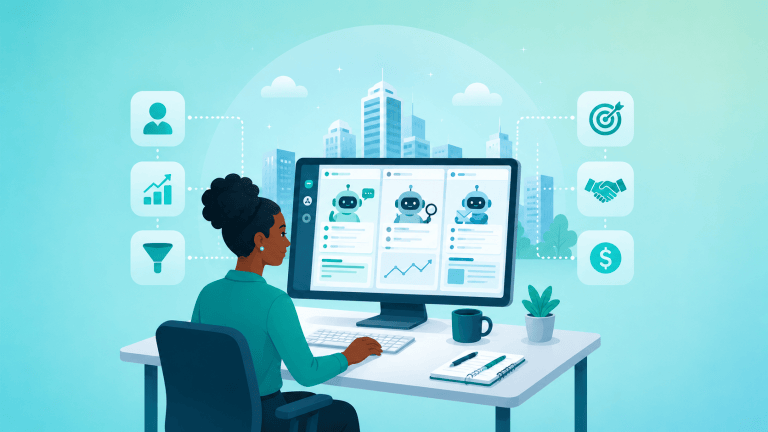
A rapidly expanding percentage of the automated traffic hammering modern e-commerce websites consists of artificial intelligence assistants, large language model (LLM) scrapers, and AI-powered search agents. These bots belong to next-generation discovery platforms—such as OpenAI’s ChatGPT, Anthropic’s Claude, and Perplexity—that consumers increasingly rely upon for personalized product recommendations and transactional assistance.
This shift forces digital merchants into a complex balancing act. Block all bots indiscriminately, and a brand risks rendering itself invisible on the very discovery channels that drive high-intent, modern consumer traffic. Leave bot traffic completely unmanaged and unmonitored, however, and retailers face severely degraded server performance, inflated operational costs, and dangerously skewed data analytics. Consequently, digital commerce leadership is being forced to pioneer a sophisticated, nuanced bot mitigation strategy: allowing the right AI crawlers in to foster brand visibility while aggressively locking out malicious agents that drain resources and inflate enterprise risk.
Chronology: How Automated Traffic Transformed the Digital Marketplace
Phase One: The Wild West of Web Scraping (Late 2000s – Mid 2010s)
In the early days of scaled e-commerce, bots were rudimentary. Competitors used basic screen scrapers to monitor pricing matrices, while early scalpers deployed primitive scripts to bypass purchase limits on limited-edition goods. Security architecture during this period focused primarily on straightforward IP blacklisting and rudimentary CAPTCHA challenges at the checkout gate.
Phase Two: The Rise of Credential Stuffing and Distributed Threats (Mid 2010s – 2020)
As APIs became foundational to modern web architecture, bot technology evolved into sophisticated, distributed cyber-attacks. Criminal syndicates deployed botnets capable of rotating residential proxies to mimic human browsing behavior, utilizing automated credential stuffing to hijack dormant user accounts and monetize stored payment methods. Security posture shifted toward cloud-based Web Application Firewalls (WAFs) and behavioral analysis.
Phase Three: The Generative AI Boom and the Dual-Use Dilemma (2022 – Present)
The explosive public adoption of generative AI in late 2022 fundamentally changed the calculus of web traffic. Suddenly, millions of consumers stopped using traditional search engines, turning instead to conversational LLMs to find products, compare specifications, and curate gift lists.
Simultaneously, AI companies began deploying hyper-efficient crawlers to index the web at unprecedented scales. E-commerce platforms found themselves wrestling with a profound paradox: the automated agents knocking at their virtual doors were no longer just adversaries trying to steal inventory—they were crucial business partners driving top-of-funnel customer discovery.
Supporting Data & The High Stakes of Mismanaged Traffic
The financial and operational implications of failing to manage this traffic are profound. Industry analyses highlight several critical vulnerabilities facing digital retailers today:
- Analytics Distortion: Automated scripts and bots routinely account for a massive, often invisible percentage of total web sessions. When non-human visitors inflate session counts, they severely skew conversion rates, average order values (AOV), and traffic acquisition metrics.
- Wasted Ad Spend: Marketing leaders relying on distorted analytics run the risk of misallocating significant advertising budgets to chase phantom audiences that were never composed of real human buyers.
- Server Strain and Latency: Unchecked LLM crawlers frequently run deep, repetitive, recursive queries across complex product catalogs, filter combinations, and pagination structures. This places an unsustainable burden on origin servers, leading to sluggish site speeds that actively drive real, high-intent shoppers away.
- The Cyber Week Collision: Peak shopping events—most notably the run-up from Thanksgiving through Cyber Monday—represent the ultimate collision course between human shoppers and automated traffic. During these high-stakes windows, real buyers flood sites concurrently with aggressive scrapers, scalpers, and AI indexing agents. Without proactive mitigation, storefronts buckle under the combined load.
Official Responses and Strategic Frameworks
Addressing this intricate challenge requires acknowledging that bot mitigation is not a task for a single department or a standalone software toggle. Industry experts emphasize that it is a shared responsibility spanning internal engineering teams, e-commerce platform providers, and Edge Content Delivery Network (eCDN) partners.
While third-party vendors and eCDNs supply the foundational architecture to withstand baseline attacks, enterprise architects must actively monitor, configure, and tune their own application environments.
A Layered Defense Framework
There is no single "magic switch" capable of instantly separating beneficial AI discovery traffic from predatory scraping bots. Effective mitigation demands a multi-tiered defense strategy:
1. Edge Defense (eCDN and WAF Configuration)
Edge defense serves as the frontline security gatekeeper. Many protective measures are fully self-service, allowing engineers to deploy them instantly without administrative friction. These include:
- Custom Web Application Firewall (WAF) rules
- Granular rate limiting based on request velocity
- IP, Autonomous System Number (ASN), and geographic blocking
- Managed Challenges and emergency "Under Attack" modes
- Automated Waiting Rooms designed to absorb traffic spikes during flash sales
However, heavier enterprise tools—such as Advanced Bot Management, Turnstile, and Precursor security layers—require deliberate evaluation. Because these tools carry real tradeoffs in cost, compatibility, and latency, they are particularly sensitive for merchants operating complex stacked-CDN architectures.
Crucial Engineering Rule: Security teams must always test newly drafted edge rules in "log-only mode" before promoting them to active blocking. A hastily deployed rule can accidentally sever access for legitimate AI search engines and search engine indexers, instantly harming organic brand discovery.
2. Application-Level Hardening
While edge defense stops malicious traffic at the perimeter, application-level hardening protects the interior infrastructure.
- Optimized
robots.txtFiles: Retailers must move beyond default configurations. Therobots.txtfile should be treated as a precise directional guide for well-behaved crawlers regarding site structure—though teams must remember it acts as polite guidance, not an impenetrable security control. - Securing High-Value Endpoints: Mission-critical, database-heavy pages—such as user login portals, checkout funnels, account creation forms, and complex search/filter parameters—require strict rate limiting and aggressive smart caching. Introducing invisible friction, such as modern browser challenges on high-value forms, dramatically raises the cost of automated abuse without alienating real human shoppers.
3. Analytics Integrity and Server-Side Validation
To protect marketing investments and performance reporting, enterprises must implement server-side event tracking and validation. By filtering out non-human visits before they hit core reporting dashboards, organizations ensure that personalization engines, customer data platforms (CDPs), and executive dashboards reflect genuine consumer behavior rather than noisy bot traffic.
Implications for the Future of Retail and E-Commerce Architecture
The evolution of automated web traffic signals a permanent maturation of the digital retail landscape. Brands that successfully navigate this transition will master a delicate equilibrium: they will open their digital storefronts wide enough to be discovered, indexed, and recommended by the AI assistants shaping modern consumer habits, while slamming the door shut on malicious actors attempting to exploit system vulnerabilities.
Achieving this balance requires an operational shift away from reactive fire-fighting toward proactive, continuous architecture tuning. As peak shopping seasons grow increasingly volatile, retail organizations that establish these sophisticated filtering muscles early will enter high-traffic periods with high-performing, resilient storefronts and absolute clarity over who is visiting their sites.
Ultimately, the future belongs to the brands that recognize that not all automated traffic is an enemy—and that turning smart bot management into a strategic core competency is no longer optional for modern digital commerce success.



