










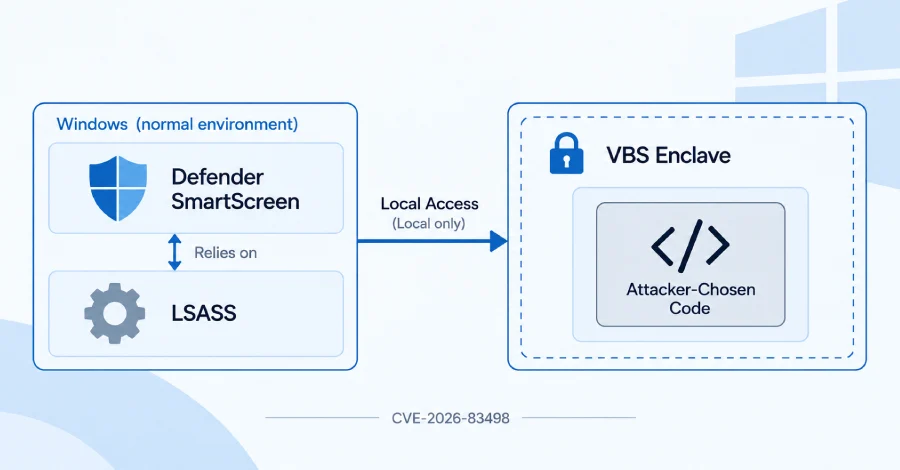
WASHINGTON — In a milestone demonstration of advanced systems hacking, security researchers have successfully executed arbitrary code inside one of the most heavily guarded compartments of the Microsoft Windows operating system: a Virtualization-Based Security (VBS) enclave.
The breakthrough, achieved in a controlled laboratory environment, targeted a specialized memory region specifically engineered to remain entirely sealed off from compromise—even in catastrophic scenarios where an attacker has achieved total administrative control over the rest of the host computer.
While the technique represents a proof-of-concept rather than an active in-the-wild campaign, it highlights both the extraordinary ingenuity of modern vulnerability research and the persistent challenges of securing hardware-isolated virtual environments. Microsoft has since addressed the core vulnerability, but the investigation has triggered a broader debate regarding how operating systems manage legacy components and the looming threat of "bring your own vulnerable enclave" tactics.
Main Facts: Piercing the Virtual Iron Curtain
At the heart of the research is the compromise of a VBS enclave—an isolated slice of memory managed by the Windows hypervisor to guard sensitive data, such as cryptographic keys and authentication tokens. Specifically, the researchers focused on SFAPE.dll, the internal component powering the Enhanced Phishing Protection feature within Microsoft Defender SmartScreen.
This security mechanism is designed to monitor text typed or pasted across applications, warning users if they accidentally enter their Windows sign-in credentials into unauthorized locations, such as untrusted web forms or generic text editors like Notepad. To perform this verification without exposing the plaintext password to the wider operating system, Windows intercepts credentials during login, hashes them, and stores them securely within the VBS enclave.
The research team, hailing from the security firm Doyensec, managed to chain multiple subtle software flaws to breach this barrier. By manipulating an initialization routine and exploiting a subsequent timing anomaly, the researchers bypassed the enclave’s memory protection boundaries. This allowed them to execute custom, attacker-selected code inside the isolated environment—a region conceptually insulated from normal system code (VTL0) by operating in a trusted, hypervisor-enforced layer known as VTL1 or Isolated User Mode.
Tracking data indicates the vulnerability is cataloged as CVE-2026-83498. Microsoft has classified the issue as an elevation-of-privilege vulnerability with a "Critical" severity rating and a Common Vulnerability Scoring System (CVSS) score of 7.8.
Crucially, the attack vector is strictly local. It cannot be exploited remotely over a network; instead, it requires an adversary to already possess low-level access and a foothold on the local machine—specifically, the ability to interact with the local process (lsass.exe) that loads and calls the targeted enclave.
Chronology of Discovery and Remediation
The timeline surrounding CVE-2026-83498 details a coordinated effort between internal engineering teams and external vulnerability researchers:

- September 8, 2026: Microsoft officially issues its monthly cumulative security updates—including update KB5124008 for Windows 11 (versions 24H2 and 25H2)—which silently incorporates a patch for the SFAPE enclave vulnerability.
- October 13, 2026: Doyensec publicly publishes its technical breakdown of the research, detailing the exact mechanism by which the VBS enclave isolation was bypassed over a month after the patch had been deployed to end-user systems.
- Post-Patch Era: Security analysts comparing the pre- and post-patch binaries discover that Microsoft’s remediation involved implementing stricter address validation checks prior to initialization, alongside modifications to mitigate the timing bugs leveraged in the exploit chain. Additionally, a new policy was introduced to block older, vulnerable iterations of the SFAPE enclave from loading entirely.
Supporting Data: Dissecting the Exploit Chain
The attack formulated by Doyensec did not rely on a single, catastrophic programming blunder. Rather, it represents a masterclass in chaining minor implementation errors into a comprehensive system compromise.
1. The Initialization Flaw
The attack began with a quirk in the enclave’s Initialize function. Ordinarily, calling this function a second time is restricted or handled gracefully. However, the researchers discovered that invoking it repeatedly forced the enclave to write a fixed, four-byte error value into a memory address explicitly controlled by the calling program, while simultaneously skipping the strict address validation checks performed during the initial call.
Doyensec researchers were careful to note that characterizing this initial behavior alone as an "arbitrary write" would be a substantial exaggeration. However, when directed precisely at internal memory tracking structures, that single constrained write successfully corrupted the value the enclave relied on to distinguish its own memory space from that of the host operating system. Consequently, its internal safety and integrity checks effectively flatlined.
2. Timing Bugs and Memory Manipulation
With the primary boundary check degraded, the researchers targeted a timing bug residing in a separate enclave function. This flaw triggered a controlled memory wipe, manipulating how the enclave looked up stored objects. The resulting read-and-write primitives gave the team the leverage needed to overwrite the internal function lookup table—the very mechanism dictating which authorized code sequences the enclave was permitted to execute.
By substituting this table, the researchers successfully achieved arbitrary code execution inside the protected VBS enclave, neutralizing the architectural guarantees of Isolated User Mode.
3. Impact Assessment
While the research shattered the theoretical and practical isolation of the SFAPE enclave, Doyensec emphasized that the exploit did not directly demonstrate the mass extraction or theft of user passwords. In alignment with this, Microsoft’s official advisory categorizes the primary impact strictly as potential "data leakage from or code execution inside the enclave," rather than an active credential-harvesting exploit observed in the wild.
Official Responses and Remediation Status
Microsoft’s security response center confirmed that the issue was identified both through internal auditing and external disclosure via Doyensec.
To mitigate CVE-2026-83498, Microsoft rolled out cumulative updates requiring administrators and consumers to apply the standard September 2026 patch cycle. The fix implements two primary defenses:
- Code Hardening: The vulnerable
SFAPE.dllbinary was updated to enforce strict address validation before executing memory writes during initialization, alongside patches neutralizing the timing vulnerability. - Enclave Blocklisting Policy: The update deploys a policy enforcement mechanism designed to prevent the loading of known vulnerable versions of the SFAPE enclave.
Because VBS enclaves are loaded locally by host processes, traditional workarounds are largely ineffective. System administrators have been advised to ensure all Windows 11 endpoints are running the latest cumulative updates.

Implications: The Looming Threat of Enclave Abuse
While the immediate vulnerability discovered by Doyensec has been patched, security experts warn that the broader implications of the research expose a systemic blind spot in modern operating system architecture.
The Missing Blocklist
A glaring issue highlighted by the research is the lack of a centralized, comprehensive blocklist for vulnerable enclaves within Windows. While Microsoft successfully blocked the outdated iteration of the SFAPE enclave via its September policy update, other historical enclave vulnerabilities remain unaddressed by similar system-wide blocks.
For instance, Doyensec pointed out that an older Microsoft Edge enclave featuring a remarkably similar read-and-write flaw—tracked as CVE-2023-36880 from 2023—is still technically permitted to load on standard systems. It remains unclear whether this oversight stems from an administrative omission or deliberate design choices concerning software compatibility.
"Bring Your Own Vulnerable Enclave"
This discrepancy carries profound security implications. In recent years, offensive security researchers—including independent analyses published by firms such as Akamai and Outflank—have warned about an emerging attack technique known as "Bring Your Own Vulnerable Enclave" (BYOVE).
Analogous to the well-documented "Bring Your Own Vulnerable Driver" (BYOVD) tactics used by advanced persistent threat (APT) groups and ransomware operators, BYOVE involves threat actors deliberately introducing legitimate, digitally signed, but inherently flawed enclaves into a compromised target environment. Because these files are cryptographically signed by trusted entities (such as Microsoft or major software vendors), security solutions and operating system kernels frequently permit them to load. Once loaded, attackers leverage known bugs within those legacy components to conceal malicious code, evade endpoint detection and response (EDR) agents, and shield administrative payloads inside high-privilege virtual enclaves.
By leaving historical, vulnerable enclaves unblocked while patching active system components, operating system architectures may inadvertently leave the door open for sophisticated threat actors to weaponize legacy code against the very security boundaries designed to protect enterprise environments.
As hardware-based isolation technologies like VBS, Intel SGX, and AMD SEV become increasingly central to modern endpoint and cloud security, the Doyensec research serves as a stark reminder: building impenetrable virtual walls is only half the battle; maintaining and consistently pruning the integrity of everything allowed inside those walls remains an ongoing, high-stakes arms race.



