By Investigative News Desk
Published: October 2026
Main Facts
Federal Bureau of Investigation (FBI) agents arrested a prominent Canadian cybersecurity executive in Pennsylvania in connection with an intensifying, high-stakes investigation into the notorious ShinyHunters cybercrime syndicate. The suspect has been identified in federal court documents as Edward Dubrovsky, an industry veteran who specializes in ransomware negotiations, incident response, and cyber extortion advisory.
The arrest follows a series of dramatic escalations involving the ShinyHunters group, which recently claimed responsibility for a massive breach of FBI systems. The syndicate allegedly siphoned sensitive, restricted personnel data—including operational unit details, specialized assignments, and confidential medical and psychiatric records—pertaining to thousands of federal agents.
According to multiple sources close to the ongoing federal investigation, Dubrovsky was apprehended while visiting Philadelphia to attend the high-profile Cyber Risk Summit, an industry conference where his firm served as a primary corporate sponsor. Federal court records indicate that Dubrovsky was taken into custody on October 8, 2026, facing serious criminal counts, including conspiracy to commit cyber extortion and interference with commerce by threats.
While the core investigative complaint and supporting affidavits remain sealed by federal authorities, publicly indexed court documentation highlights the gravity of the charges. The case—initially docketed in Pennsylvania—has already been ordered transferred to the U.S. District Court for the Eastern District of Texas, which sources confirm has become the centralized command center and epicenter for the nationwide, multi-agency ShinyHunters task force.
Chronology of Events
The sprawling international dragnet and subsequent arrest of Dubrovsky represent the culmination of weeks of rapidly accelerating law enforcement operations spanning North America and Europe. The timeline of key developments underscores the unprecedented nature of the conflict between federal cyber-investigators and the ShinyHunters collective:

- September 2026: Law enforcement operations reach a critical milestone when Dutch National Police, acting on intelligence supplied by international partners, arrest Pepijn van der Stap, a reformed cybercriminal linked to the infrastructure of the ShinyHunters group. Investigators immediately seize a treasure trove of digital devices, which FBI forensic specialists begin poring over.
- Late September 2026: Following Van der Stap’s arrest, a volatile internal shift occurs within the ShinyHunters hierarchy. A prominent syndicate member operating under the alias "Rey" assumes operational control of the group. In an unprecedented display of cyber-defiance, "Rey" begins publicly taunting federal authorities, leaking compromised troves of data stolen from the FBI’s proprietary online recruitment portal.
- Early October 2026: Global cybersecurity firms and insurance executives gather in Philadelphia, Pennsylvania, for the annual Cyber Risk Summit at the Loews Philadelphia Hotel (held October 5–7). Among the attendees and top-tier sponsors is Edward Dubrovsky, representing the Canadian security and advisory firm CyberSteward.
- October 7, 2026: Reuters and investigative journalists break the news that "Rey"—subsequently identified as a teenage individual named Saif Al-din Khader—has been detained by authorities and is actively cooperating with FBI investigators. Khader’s apprehension occurs as the group attempts to orchestrate a high-profile extortion campaign against a digital aviation and navigation unit recently divested by aerospace giant Boeing.
- October 8, 2026: Federal law enforcement agents arrest Edward Dubrovsky in Pennsylvania. Court records officially index the charges under the name Edward Dobrovsky, noting felony counts related to extortion conspiracy and threat-based commerce interference.
- October 9, 2026: Federal courts file a formal transfer notice, moving Dubrovsky’s prosecution from Pennsylvania to the Eastern District of Texas, aligning the case directly with the primary federal task force handling the broader ShinyHunters syndicate. Concurrently, public relations representatives for his former employer, Cypfer, issue statements clarifying his executive timeline and departure dates.
Supporting Data and Background
The arrest of a high-profile incident response executive sheds light on the murky, high-stakes intersection between commercial ransomware negotiation firms and the global cybercrime underground.
The Profile of the Accused
Edward Dubrovsky is a recognized figure within the North American cybersecurity ecosystem. Prior to his association with the firm CyberSteward, Dubrovsky served in senior leadership roles at Cypfer, a prominent Canadian security company specializing in handling ransomware remediation and extortion negotiations. Cypfer’s public relations representatives later clarified that Dubrovsky served as a managing director prior to his resignation in December 2025, pushing back against LinkedIn profile assertions that he was an original company co-founder.
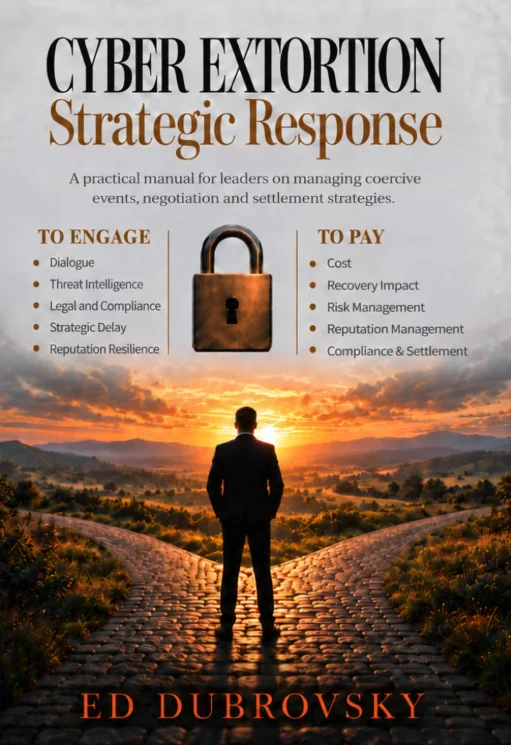
Beyond his corporate advisory work, Dubrovsky is the author of Cyber Extortion Strategic Response, a 252-page manual designed to guide corporate executives through the complex calculus of ransomware incidents. An excerpt from the book’s official listing highlights a core operational philosophy taught within the industry:
"At the heart of the book is a critical distinction: communicating with a criminal is not the same as negotiating a payment, and negotiating is not a commitment to pay. Engagement can serve other objectives, including testing claims, gathering information, creating time, and preserving options while the organization evaluates its next move."
Despite these published strategies, federal prosecutors now allege that Dubrovsky crossed the legal and ethical boundary separating advisory communication from active criminal conspiracy and extortion.
The Anatomy of ShinyHunters
The ShinyHunters syndicate is internationally recognized for its aggressive modus operandi. The group typically targets software-as-a-service (SaaS) providers and corporate entities via advanced phishing campaigns and credential-stuffing attacks. Once inside a network, the actors siphon vast repositories of proprietary and confidential data, leveraging the threat of public exposure to extort massive cryptocurrency payouts.

According to cumulative FBI intelligence metrics, the group has successfully extorted upward of $70 million from corporate victims globally throughout the current year alone. However, their decision to target federal law enforcement personnel—specifically compromising the FBI’s online recruitment database containing sensitive medical, psychological, and specialized assignment histories—marked a catastrophic miscalculation that galvanized the full might of U.S. national security apparatuses.
Official Responses and Industry Reactions
As the fallout from the arrests ripples across the cybersecurity community, official channels have maintained a tightly controlled posture, while corporate entities scramble to distance themselves from the unfolding scandal.
- The FBI and Director Kash Patel: Federal law enforcement leadership has maintained a guarded stance regarding the specifics of the ongoing prosecution. While FBI Director Kash Patel acknowledged the general crackdown via a brief statement published on social media platform X (formerly Twitter), the bureau formally declined to provide detailed comments to investigative reporters regarding the evidentiary links between Dubrovsky and the ShinyHunters enterprise.
- Cypfer Corporate Statement: In response to media inquiries regarding Dubrovsky’s professional background, Cypfer issued a clarifying statement emphasizing that Dubrovsky severed his ties with the organization in late 2025. The firm reiterated its commitment to legal compliance and ethical ransomware remediation standards.
- Legal Representation: Court docket reviews indicate that as of the latest filings, Dubrovsky has not retained private defense counsel, nor has a public defender been formally appointed by the presiding federal magistrate judge. He remains detained at a federal holding facility in Philadelphia pending his physical transfer to the Eastern District of Texas.
Implications for the Cybersecurity Industry
The arrest of a leading ransomware negotiation executive marks a watershed moment for the global cybersecurity and cyber-insurance sectors. For years, the multi-billion-dollar incident response industry has operated in a heavily grey regulatory landscape, where specialized firms act as intermediaries between multinational corporations and violent cybercrime syndicates to facilitate ransom payouts.
Redrawing the Legal Boundaries
Law enforcement’s aggressive targeting of an advisory executive signals that federal prosecutors are scrutinizing the methods utilized by private negotiation firms. The criminal complaint—charging conspiracy to threaten the confidentiality of data for extortion—raises existential questions for the industry:
- The Compliance Tightrope: Where does lawful intelligence-gathering and threat-actor communication end, and illegal facilitation of extortion begin?
- Regulatory Overreach vs. Accountability: As state-sponsored and financially motivated syndicates increasingly target critical infrastructure and national security agencies, governments are signaling zero tolerance for private entities that maintain unregulated financial pipelines to criminal networks.
Looming Indictments
According to deep-cover sources within the investigative framework, federal investigators are continuing to analyze the digital evidence seized from Pepijn van der Stap’s Dutch residence, alongside devices secured during recent operations. Analysts warn that Dubrovsky’s arrest may not be an isolated incident; additional criminal charges against principals and executives at other specialized ransomware negotiation firms are widely anticipated in the coming weeks.
As this fast-moving legal and investigative saga unfolds, the cybersecurity sector faces an uncomfortable reckoning, forced to re-evaluate the legal risks, operational boundaries, and moral hazards inherent in managing the modern epidemic of digital extortion.