

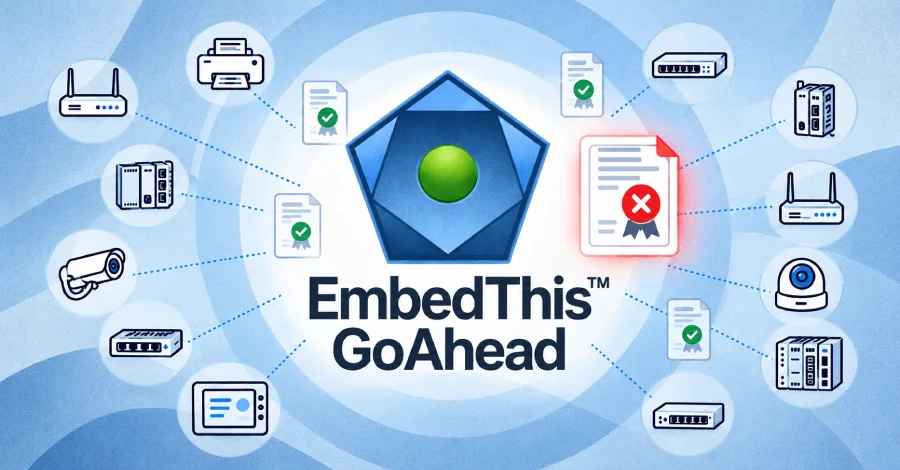
Global Supply Chain Warning: A trio of cryptographic vulnerabilities in the ubiquitous GoAhead embedded web server leaves countless industrial controllers, enterprise printers, routers, and IoT gateways exposed. Security researchers urge device manufacturers to expedite firmware patches. Main Facts The cybersecurity landscape faces a sweeping challenge following the disclosure of three high-severity Transport Layer Security (TLS) […]
White House Launches ‘Project Lifeline 250’ to Shield Vulnerable Rural Hospitals from Rising Cyberthreats
WASHINGTON & COLUMBIA, S.C. — In a decisive move to fortify America’s most vulnerable medical facilities against sophisticated digital adversaries, the Office of the National Cyber Director (ONCD) has officially rolled out its second regional cybersecurity pilot program. Dubbed Project Lifeline 250, the new six-month initiative is specifically tailored to protect rural hospitals by bridging […]
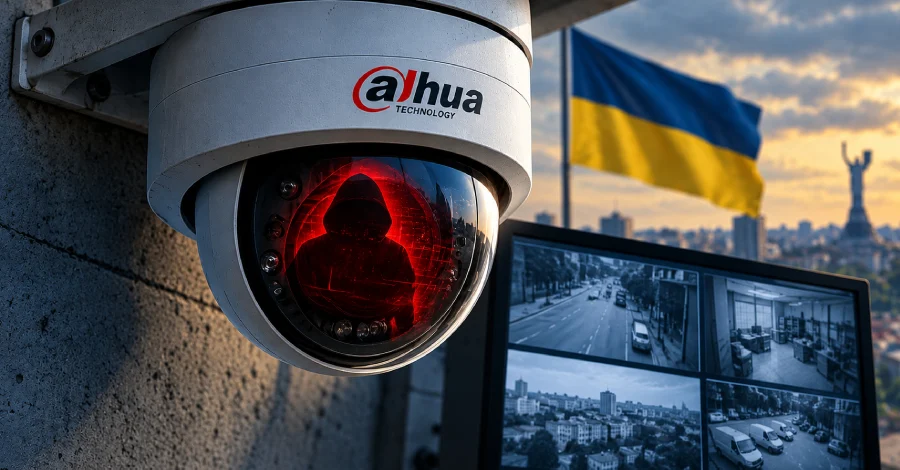
Critical Alert: Mass Compromise of Dahua IP Cameras Exposes European and Ukrainian Infrastructure to Russian Espionage
KYIV / THE HAGUE — In an escalating cyber-espionage conflict running parallel to kinetic warfare, cybersecurity authorities in Ukraine have issued an urgent warning regarding widespread, unauthorized remote access to video surveillance systems manufactured by Dahua Technology. The Computer Emergency Response Team of Ukraine (CERT-UA), operating under the auspices of the State Special Communications Service […]
Massive "Gheist" Campaign Weaponizes Stolen GitHub Tokens Across 13,500+ Branches in Sophisticated Supply Chain Attack
GLOBAL CYBERSECURITY BULLETIN — Cloud security researchers have uncovered and disrupted a sprawling, highly automated campaign that systematically targeted thousands of GitHub repositories. Dubbed "Gheist," the operation utilized stolen access tokens to plant malicious, secret-stealing GitHub Actions workflows across more than 13,500 individual branches. The campaign underscores a dangerous evolution in software supply chain attacks, […]
The Great Consolidation: Jonathan Care on the Future of AI Security
The cybersecurity landscape is currently undergoing a structural transformation that mirrors the chaotic, high-stakes maturation of the early fraud detection market. According to Jonathan Care, Lead Analyst and Practice Lead for AI at KuppingerCole Analysts, the current frenzy of AI security startups is a precursor to a massive, inevitable wave of industry consolidation. In a […]
Secret Court Opinion Sparks Congressional Showdown as Section 702 Surveillance Authority Hangs in the Balance
WASHINGTON — A high-stakes legislative and legal battle is intensifying on Capitol Hill over the future of federal intelligence gathering, centered on a classified Foreign Intelligence Surveillance Court (FISC) opinion that the Trump administration is now more than a month overdue in releasing. The delayed declassification has ignited fierce pushback from a bipartisan coalition of […]
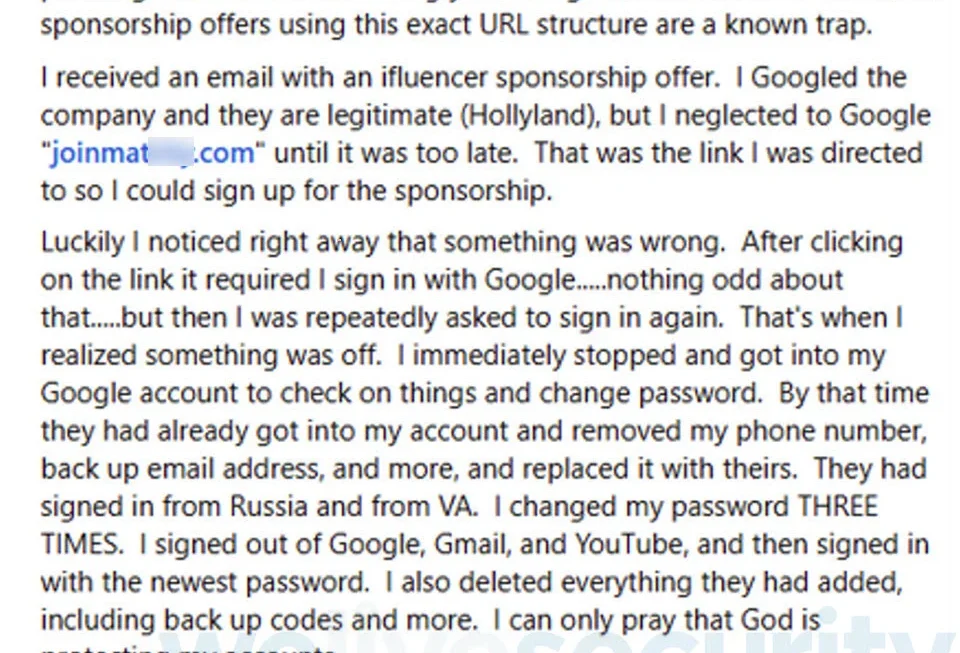
The Sponsorship Trap: How Sophisticated Phishing Campaigns Are Hijacking YouTube Creators
For the modern content creator, a sponsorship email is the digital equivalent of a golden ticket. It represents validation, growth, and the professionalization of a passion project. However, beneath the surface of these professional-looking inquiries lies a growing, systemic threat that can dismantle a creator’s career in a matter of seconds. A sophisticated, modular phishing […]
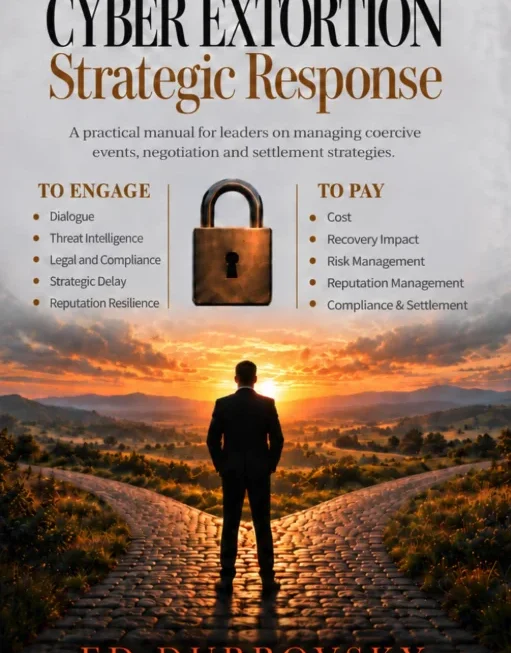
Executive at Canadian Cybersecurity Firm Arrested in Pennsylvania Amid Escalating FBI Probe into ShinyHunters Syndicate
By Investigative News Desk Published: October 2026 Main Facts Federal Bureau of Investigation (FBI) agents arrested a prominent Canadian cybersecurity executive in Pennsylvania in connection with an intensifying, high-stakes investigation into the notorious ShinyHunters cybercrime syndicate. The suspect has been identified in federal court documents as Edward Dubrovsky, an industry veteran who specializes in ransomware […]
CISA Shifts to "Aggressive, Anticipatory" Defense in Landmark 2030 Strategy for US Critical Infrastructure
WASHINGTON — In a profound departure from decades of traditional cybersecurity doctrine, the US Cybersecurity and Infrastructure Agency (CISA) has officially committed to abandoning what it calls “passive defense.” Under a newly unveiled roadmap, the agency is pivoting toward an aggressive, anticipatory posture designed to neutralize modern cyber-threats before they can paralyze American critical infrastructure. […]
Experts temper emergency-level alarms over critical Brotli defect
By Global Technology & Cybersecurity Desk Published: October 2026 Main Facts A high-severity security defect tracked as CVE-2026-111497—widely dubbed "Node2Shell" or "Broccoli2Shell"—has triggered an emergency response across the global technology sector. The vulnerability resides within the Brotli decompression library, a data compression tool originally developed by Google that has become a ubiquitous foundational component embedded […]