

GLOBAL CYBERSECURITY BULLETIN — Cloud security researchers have uncovered and disrupted a sprawling, highly automated campaign that systematically targeted thousands of GitHub repositories. Dubbed "Gheist," the operation utilized stolen access tokens to plant malicious, secret-stealing GitHub Actions workflows across more than 13,500 individual branches. The campaign underscores a dangerous evolution in software supply chain attacks, […]
Beyond the Install Script: How the indexed-btree Campaign Exposes the Limits of Modern Software Supply Chain Security
By Global Technology & Cybersecurity Desk For years, software security engineering operated on a comforting, albeit increasingly fragile, assumption: if a third-party package installed cleanly without triggering a suspicious life-cycle script, the immediate danger had passed. In the ecosystem of the JavaScript package manager, npm, developers learned to eye pre-install and post-install hooks with deep […]
Massive Global Token-Spraying Campaign Exploits Microsoft 365 Environments in Sophisticated BEC Operation
By Global Cybersecurity Desk Published: October 2026 Main Facts A newly uncovered, highly coordinated global cyber-espionage and financial crime campaign has targeted corporate Microsoft 365 (M365) environments in an automated operation that launched hundreds of thousands of unauthorized access attempts worldwide. Discovered and analyzed by threat intelligence researchers at cybersecurity firm Huntress, the campaign relied […]
Out of Site, Out of Mind: Best Practices for Creating Valuable On-Site Campaign Content
Main Facts: The Modern PR Dilemma and the Pivot to On-Site Value In the fast-paced world of modern public relations, campaigns have traditionally looked outward. Public relations teams pour immense resources into external outreach, desperate to secure coveted coverage, features, and mentions in high-authority third-party publications. However, this hyper-focus on external real estate often comes […]
Notorious Russian Military Hackers Target NATO Defense and Law Enforcement in Sophisticated Espionage Campaign
WASHINGTON — In a chilling reminder of the persistent and evolving threat posed by state-sponsored cyber espionage, a hacking group tied directly to Russian military intelligence has successfully infiltrated critical defense contractors and a law enforcement agency within NATO member states. According to threat intelligence researchers at Symantec, the campaign—tracked under the moniker Swallowtail—is the […]
Call of Duty: Modern Warfare 4 Campaign Review — A Triumphant Return to Form or a Flawed Flashpoint?
Main Facts: The Resurgence of Infinity Ward’s Flagship Franchise Following the critical misfire and widespread fan backlash of 2023’s Modern Warfare 3—widely criticized for its rushed, Warzone-padded single-player offering—Infinity Ward has returned with Call of Duty: Modern Warfare 4. Spanning a robust 16-mission campaign, the new release seeks to restore the narrative soul and tactical […]
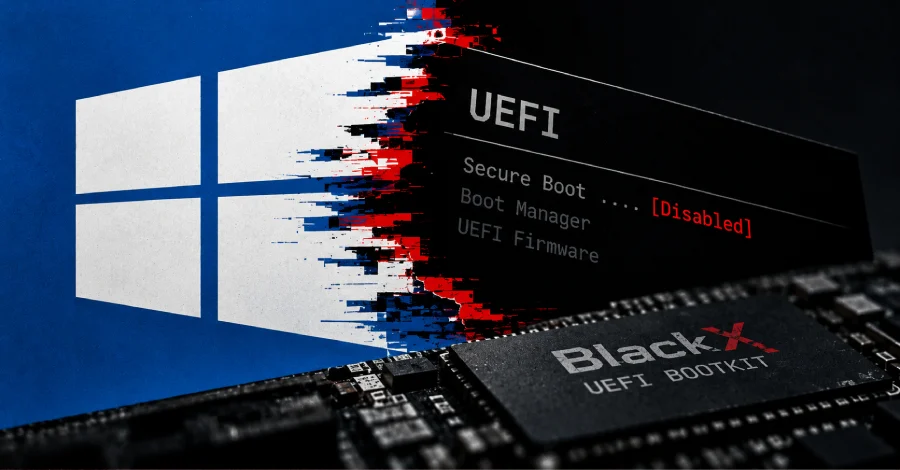
Sophisticated "BlackX" UEFI Bootkit Targets Central Asian Diplomats in State-Sponsored Cyber Espionage Campaign
By Global Security Desk Published: November 2026 Main Facts: The Threat at a Glance In a chilling evolution of modern cyber espionage, high-profile diplomatic organizations across Central Asia have become the primary targets of a newly uncovered, highly sophisticated Unified Extensible Firmware Interface (UEFI) bootkit known as BlackX. Operating in the shadows of early 2026, […]
The Rise of "Token Spraying": How a Massive Campaign Bypassed MFA to Breach 79 Organizations
In a chilling demonstration of evolving cyber-adversary tactics, a sophisticated campaign recently targeted Microsoft 365 (M365) environments, successfully compromising 79 organizations without ever requiring a user’s password. By utilizing a technique researchers at Huntress have dubbed "token spraying," the attackers effectively weaponized the very session tokens designed to provide users with seamless access to their […]
The "0ktapus" Chronicles: How a Massive Phishing Campaign Exposed the Fragility of Modern MFA
In the rapidly evolving landscape of cybersecurity, the prevailing wisdom has long suggested that Multi-Factor Authentication (MFA) is the "gold standard" for securing corporate digital perimeters. However, a sprawling, sophisticated phishing campaign—dubbed "0ktapus" by researchers at Group-IB—has shattered that illusion, demonstrating that even the most robust identity and access management systems are only as strong […]
The Shadow of Pre-Disclosure: Unmasking the PHP2Shell Exploitation Campaign
In the high-stakes world of cybersecurity, the timeline of a vulnerability is typically defined by a clear, linear progression: discovery, embargo, patch release, and exploitation. However, recent findings from Amazon Web Services (AWS) have shattered this conventional wisdom. The emergence of "PHP2Shell"—a set of two critical Remote Code Execution (RCE) vulnerabilities—has revealed a disturbing trend […]