










WASHINGTON — In a chilling reminder of the persistent and evolving threat posed by state-sponsored cyber espionage, a hacking group tied directly to Russian military intelligence has successfully infiltrated critical defense contractors and a law enforcement agency within NATO member states. According to threat intelligence researchers at Symantec, the campaign—tracked under the moniker Swallowtail—is the […]
Sophisticated "BlackX" UEFI Bootkit Targets Central Asian Diplomats in State-Sponsored Cyber Espionage Campaign
By Global Security Desk Published: November 2026 Main Facts: The Threat at a Glance In a chilling evolution of modern cyber espionage, high-profile diplomatic organizations across Central Asia have become the primary targets of a newly uncovered, highly sophisticated Unified Extensible Firmware Interface (UEFI) bootkit known as BlackX. Operating in the shadows of early 2026, […]
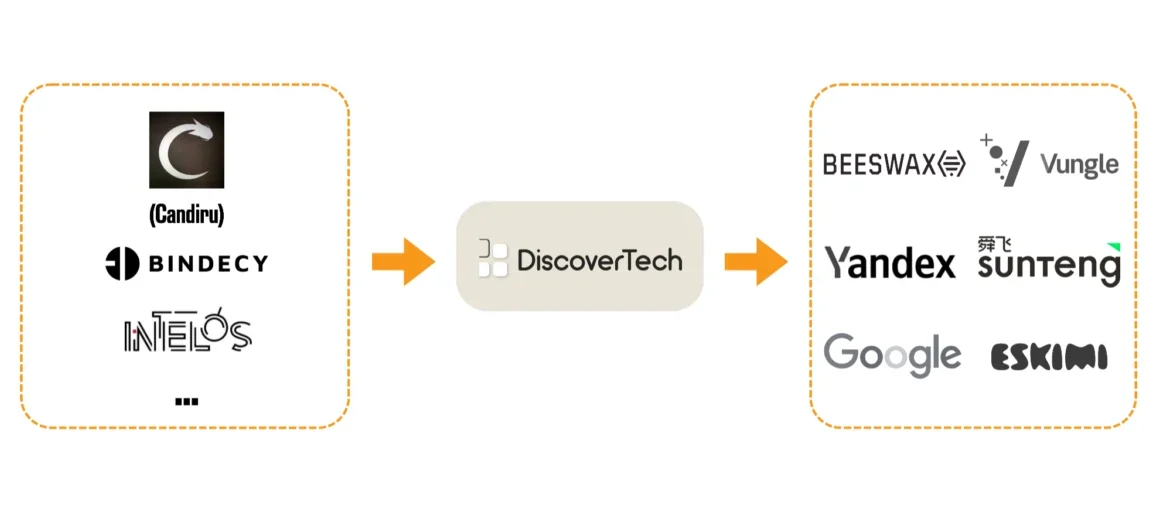
The Silent Stalkers: How Global Ad Infrastructure Became a Pipeline for High-Stakes Espionage
In the modern digital landscape, the online advertisement is often dismissed as a minor nuisance—a flickering banner for consumer goods or a fleeting distraction during a video stream. However, a groundbreaking investigation by Citizen Lab has unmasked a far more sinister reality: the world’s multi-billion-dollar advertising ecosystem has been weaponized by state-linked actors to conduct […]
High-Stakes Espionage and Corporate Warfare: OpenAI Alleges Trade Secret Theft by Returning Apple Employee
San Francisco / Cupertino — The escalating corporate cold war between tech behemoth Apple and artificial intelligence pioneer OpenAI has taken a dramatic, litigious turn. In a explosive new court filing submitted as part of an ongoing trade secrets lawsuit, OpenAI has accused a former employee of exfiltrating more than a hundred highly sensitive, confidential […]
Espionage in the Age of AI: OpenAI Engineer Arrested for Planting Secret Listening Devices
In a startling breach of corporate security that highlights the intense, high-stakes nature of the artificial intelligence industry, a 35-year-old software engineer at OpenAI has been arrested by federal authorities. Abdulrahman Alfozan, a Saudi national who joined the company in July 2025, is accused of orchestrating a clandestine surveillance operation within the company’s San Francisco […]
Corporate Espionage at the Frontier: OpenAI Engineer Arrested for Alleged Audio Surveillance Plot
In a chilling intersection of high-stakes artificial intelligence development and traditional industrial espionage, federal authorities have apprehended a software engineer at OpenAI on charges of attempting to secretly record sensitive executive deliberations. The arrest of Abdulrahman Alfozan, 35, a Saudi national who joined the San Francisco-based AI powerhouse in July 2025, has sent shockwaves through […]
U.S. Cracks Down on Beijing-Linked Cyber Espionage Network: Seven Domains Seized in Targeted Disruption
In a significant escalation of the ongoing digital cold war, the United States Department of Justice (DOJ) and the Federal Bureau of Investigation (FBI) have successfully dismantled a sophisticated hacking infrastructure linked to the Chinese state. On October 8, federal authorities announced the seizure of seven internet domains that served as the backbone for cyber […]
CISA Expands Known Exploited Vulnerabilities Catalog Amid Global Crackdown on Chinese State-Linked Espionage Infrastructure
In a significant move to fortify national security against sophisticated foreign cyber espionage, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) has formally updated its Known Exploited Vulnerabilities (KEV) catalog. The inclusion of five specific vulnerabilities—impacting ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND—marks a critical pivot in the international effort to neutralize the […]
The AI-Driven Breach: How Offensive LLMs and ARTEX Are Reshaping Financial Espionage
In a landmark case that underscores the rapid convergence of generative AI and offensive cyber operations, a sophisticated threat actor has successfully compromised multiple South Korean financial institutions. A new investigative report from CrowdStrike has unveiled a campaign—active between late September and early October 2026—that saw an attacker leverage "agentic" AI tools to conduct rapid, […]
Evolving Russian-Linked Espionage: A Deep Dive into the Two-Year Refinement of the MATCHBOIL Malware
KYIV / BRATISLAVA — Cybersecurity researchers have revealed a systematic, multi-year evolution of a cyber espionage toolset deployed against critical infrastructure in Ukraine. According to comprehensive new intelligence published by European cybersecurity firm ESET, a Russia-aligned threat actor tracked as UAC-0099 has spent at least two years steadily upgrading its custom malware, known as MATCHBOIL. […]