

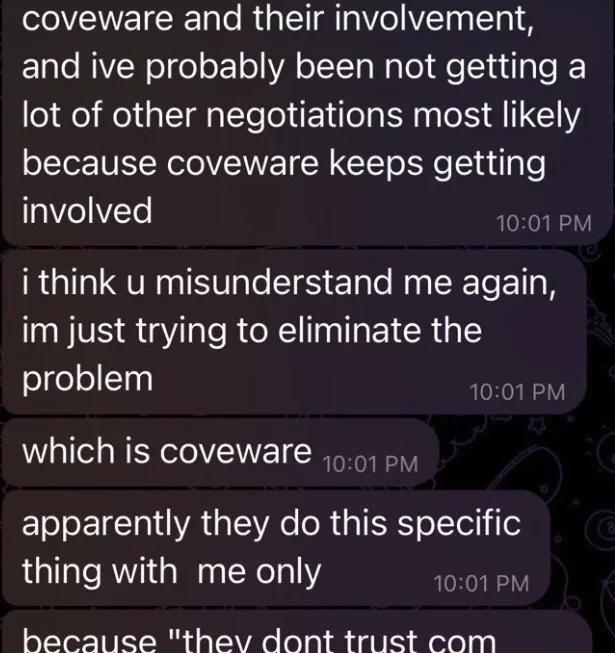
WASHINGTON — In the murky underbelly of the global cybercrime ecosystem, the lines separating those who defend networks from those who pillage them have grown dangerously blurred. A sweeping U.S. federal investigation into the notorious ShinyHunters hacking syndicate—which recently escalated its campaign by targeting the FBI itself—has exposed an alarming nexus between corporate cybersecurity executives […]
The Resurgence of Digital Extortion: Lockbit Dominates as Conti Offshoots Reshape the Ransomware Landscape
The global cybersecurity landscape is currently grappling with a significant resurgence in ransomware activity, signaling a volatile period for organizations worldwide. Following a brief springtime decline, the frequency of extortion-based cyberattacks has surged, driven by a combination of established ransomware-as-a-service (RaaS) giants and the tactical rebranding of dismantled criminal syndicates. According to the latest threat […]
The Shadow Brokers of Incident Response: How a Florida Ransomware Remediation CEO Allegedly Built a Multi-Million Dollar Double-Crossing Scheme
By Global Security Correspondent Published: October 2026 Main Facts The modern cyber-extortion economy thrives in the gray areas of digital crisis management, where panicked corporate executives, desperate to salvage operations, routinely turn to third-party intermediaries. For years, Zohar Pinhasi, a dual U.S.-Israeli national and the owner of the Florida-based ransomware remediation firm MonsterCloud, positioned himself […]
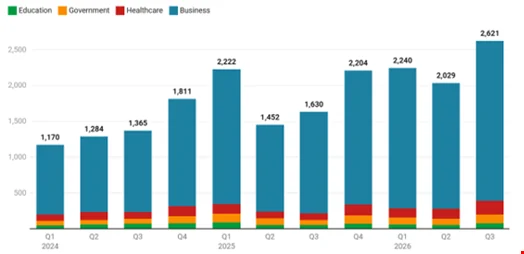
Global Ransomware Crisis Escalates to Record Highs in Q3 2026 Driven by AI Advancements and Triple-Extortion Tactics
By James Coker Published: October 2026 Main Facts The global cybersecurity landscape experienced a historic and alarming escalation during the third quarter of 2026. According to a comprehensive threat analysis published by research firm Comparitech, ransomware attacks reached their highest quarterly volume ever recorded. Between July and September 2026, threat intelligence platforms logged a staggering […]
Co-Founder of Canadian Cybersecurity Firm Arrested in High-Stakes Federal Probe Linking Ransomware Negotiators to ShinyHunters Hackers
WASHINGTON — In a dramatic escalation of a federal cybercrime investigation that has sent shockwaves through the national security apparatus, FBI agents have arrested a prominent Canadian cybersecurity executive in Pennsylvania. The high-profile arrest is directly tied to the notorious ShinyHunters hacking collective—a cybercrime syndicate that recently breached federal networks and relieved the bureau of […]
The Ransomware Mirage: MonsterCloud Owner Faces Fraud Trial for Deceptive Data Recovery Practices
The promise was simple, compelling, and—for many desperate businesses—seemingly miraculous: "We can recover your data without paying the ransom." For companies paralyzed by encrypted servers and looming operational collapse, Florida-based MonsterCloud appeared to be a white knight in the murky world of cyber-extortion. However, federal prosecutors in New York allege that this "white knight" was […]
The Resurgence of Digital Extortion: How Post-Conti Dynamics are Reshaping the Global Ransomware Landscape
The global cybersecurity landscape is currently witnessing a volatile, high-stakes reorganization. Following a brief period of apparent stagnation, ransomware activity has surged with renewed vigor. According to the latest data from the NCC Group’s Monthly Threat Pulse, the summer of 2022 has been defined by a significant uptick in successful cyber-extortion campaigns, a trend driven […]
Massive Ransomware Strike Cripples IDCF Cloud: 495 Japanese Organizations Face Prolonged Outage
In a significant blow to Japan’s digital infrastructure, IDC Frontier (IDCF), a prominent cloud and digital infrastructure provider, has confirmed it was the victim of a sophisticated ransomware attack. The breach has paralyzed operations at a critical data center cluster serving Eastern Japan, triggering a cascading impact that has affected nearly 500 companies and local […]
The Double-Victimization Scheme: How a Ransomware "Recovery Expert" Allegedly Scammed Clients for Millions
In a striking revelation that has sent shockwaves through the cybersecurity industry, the Department of Justice (DoJ) has indicted Zohar Pinhasi, the owner of the Florida-based cybersecurity firm MonsterCloud, on multiple counts of wire fraud. Pinhasi, 50, stands accused of orchestrating a sophisticated, years-long scheme that targeted organizations already reeling from the catastrophic effects of […]
New "Settra" Ransomware Variant Targets Retail and Manufacturing Sectors with Aggressive Anti-Recovery Tactics
By James Coker / Enriched Security Report Published: September 2024 Main Facts Cybersecurity researchers at Huntress have issued a high-priority warning regarding the emergence of a novel and aggressive ransomware variant dubbed Settra. First cataloged in June 2024, Settra has actively targeted organizations within the consumer services, retail, and manufacturing sectors. While researchers have documented […]