

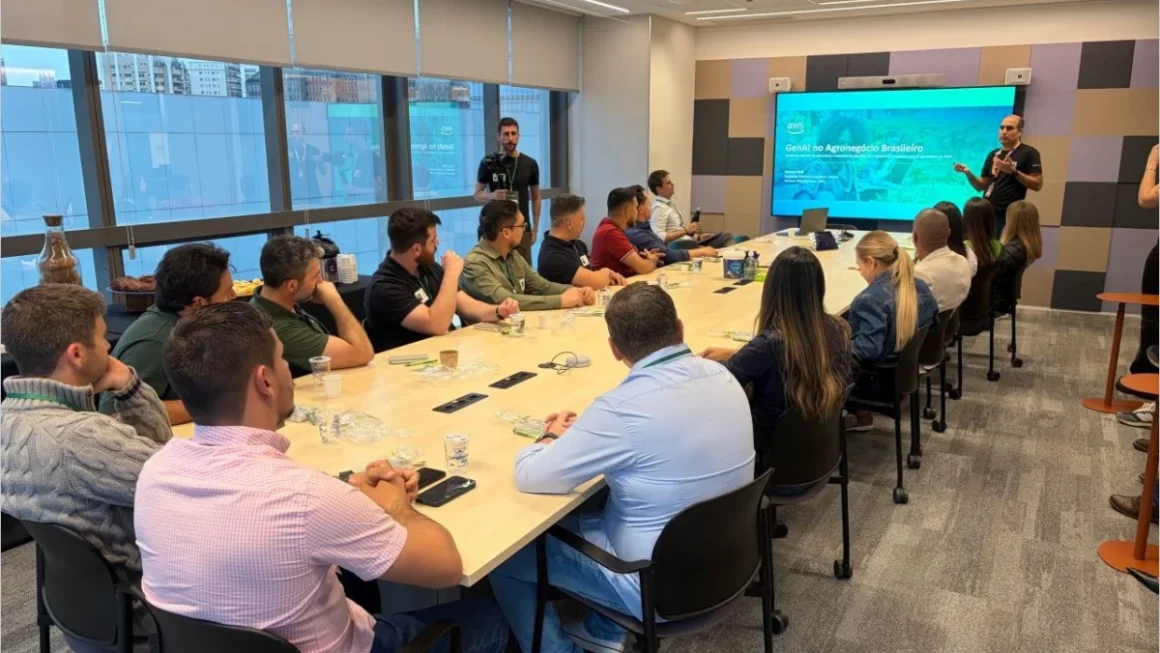
By Daniel Published as part of the AWS Weekly Roundup Series Introduction: The Real-World Velocity of Cloud Infrastructure A few weeks ago, I had the privilege of presenting to a small, focused group of commercial and technology leaders from the Brazilian agribusiness sector at the AWS office in São Paulo. My talk walked through the […]
The AI Security Paradox: Navigating the New Frontier of Web Vulnerability
Artificial Intelligence has transitioned from a buzzword to the backbone of the modern web. From streamlining content creation to optimizing server-side performance, developers and site owners are increasingly leaning on machine learning models to reduce operational costs and improve user experiences. However, the most profound—and perhaps most volatile—impact of AI is currently unfolding in the […]
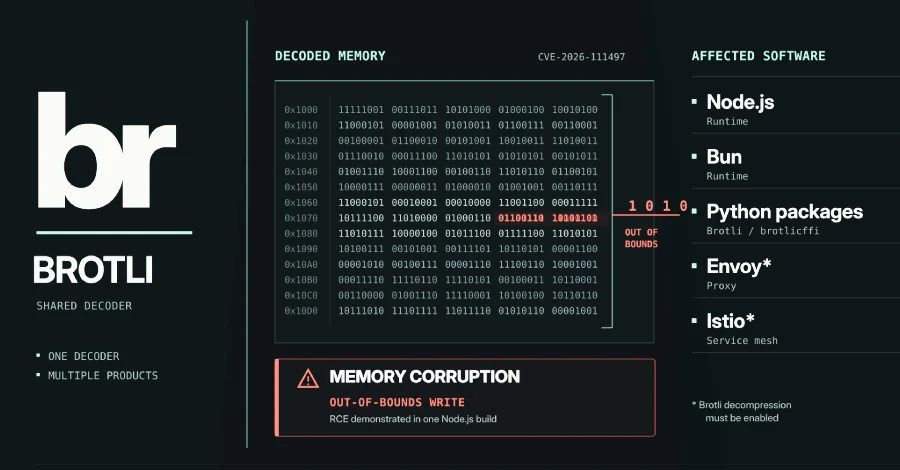
Critical Brotli Decoder Vulnerability (CVE-2026-111497) Poses Wide-Ranging Risks to Modern Web Infrastructure
By Global Tech & Cybersecurity News Desk Published: October 2026 Main Facts A high-severity memory-corruption vulnerability residing within Google’s core Brotli decompression library is currently threatening a vast swath of modern web infrastructure. Tracked officially as CVE-2026-111497, the flaw impacts virtually any software package, language runtime, or network proxy that bundles and relies on Google’s […]
The Artificial Intelligence Gold Rush for Bugs: How Automated Vulnerability Discovery is Rewriting Cybersecurity
Global Infrastructure Faces a New Era of Disruption as AI Accelerates Code Analysis, Shortens Exploit Timelines, and Triggers Urgent Industry-Wide Fire Drills Main Facts The landscape of global cybersecurity has entered a volatile and high-stakes transitional phase. According to interviews with seven leading cybersecurity professionals and upcoming research from threat intelligence firms, the rapid integration […]
Urgent Security Alert: CISA Mandates Patching for Palo Alto Networks PAN-OS Vulnerability
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a high-priority directive to federal agencies and private sector IT teams: immediate action is required to address a critical vulnerability within Palo Alto Networks’ PAN-OS firewall software. The flaw, tracked as CVE-2022-0028, has been confirmed by security researchers and the manufacturer to be under active […]
Bengaluru-Based eMudhra Winds Down Global TLS Certificate Business Following Major Security Vulnerability and Browser Distrust
Bengaluru — In a decisive strategic shift, Bengaluru-based cybersecurity major eMudhra has announced its voluntary exit from the global Secure Sockets Layer and Transport Layer Security (SSL/TLS) certificate business. The announcement comes directly on the heels of a high-profile security incident that saw browser root programs, including tech giants Google and Mozilla, withdraw their trust […]
Critical Privacy Vulnerability in Signal: Understanding the RingRTC “Ghost Call” Flaw
In an era where digital privacy is the cornerstone of secure communication, the discovery of a significant vulnerability in the Signal messaging app has sent shockwaves through the cybersecurity community. Signal, widely regarded as the gold standard for encrypted communication, recently faced a serious challenge to its reputation for total privacy. A newly disclosed flaw, […]
The Patching Paradox: Why AI-Driven Vulnerability Management Requires a Paradigm Shift
In the modern cybersecurity landscape, IT and security operations teams are engaged in a Sisyphean struggle. Every week, vulnerability scanners churn out thousands of new findings, and every month, the backlog of critical patches grows larger. For years, the industry standard response to this "patch apocalypse" has been a brute-force approach: more scans, more overtime, […]
Critical Flaw in Cisco Secure Email Gateway Under Active Exploitation: Root-Level Access Vulnerability Threatens Enterprise Networks
By Global Cybersecurity Desk Published: October 2026 Main Facts: The Zero-Day Crisis Unfolding at Cisco Cisco Systems has issued an urgent security advisory warning that threat actors are actively exploiting a critical, unauthenticated remote code execution vulnerability in the Cisco Secure Email Gateway. Tracked as CVE-2026-76519 and carrying a maximum severity CVSS score of 9.8 […]
Critical Zero-Day Vulnerability in Ivanti Connect Secure Triggers Urgent CISA Warning and Active In-the-Wild Exploitation
WASHINGTON — The United States Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent directive urging organizations worldwide to immediately update their Ivanti Connect Secure (ICS) appliances. The mandate follows the active, in-the-wild exploitation of a severe zero-day authentication bypass vulnerability. The security flaw, formally cataloged as CVE-2026-104935 with a critical CVSS score of […]