

Main Facts: The Compromise of Rank Math SEO PRO 3.0.123 In the complex ecosystem of content management systems, supply chain attacks represent one of the most insidious threats facing site administrators. Unlike traditional brute-force attacks or targeted vulnerabilities, a supply chain compromise leverages the highest level of trust: the official update channel of a legitimate, […]
Global Alert: Critical PHP Vulnerabilities Threaten Millions of WordPress Sites Worldwide
A comprehensive update to the PHP interpreter addresses two severe, remotely exploitable flaws impacting the entire WordPress and WooCommerce ecosystem. Because the vulnerability resides at the infrastructure level, traditional dashboard updates will not suffice. Executive Summary & Main Facts In a high-severity security alert that has mobilized web administrators globally, the PHP development team has […]
Bridging the AI Divide: How to Connect Self-Hosted WordPress Sites to Anthropic’s Claude via Custom Connectors
The intersection of artificial intelligence and content management systems reached a significant milestone with the widespread adoption of AI connectors. For web administrators and developers, the ability to seamlessly link an AI assistant directly to a live publishing environment unlocks unprecedented automation capabilities. A Claude connector acts as a secure, saved bridge between Anthropic’s Claude […]
Major Security Breach Exposes Over 3 Million WordPress Sites Following UpdraftPlus Server Compromise
By Cybersecurity Desk Published: October 2026 Main Facts A sophisticated and far-reaching security incident has impacted UpdraftPlus, one of the most popular backup and migration plugins in the WordPress ecosystem, installed on upwards of 3 million websites globally. The breach originated not from a coding vulnerability within the plugin itself, but rather from a security […]
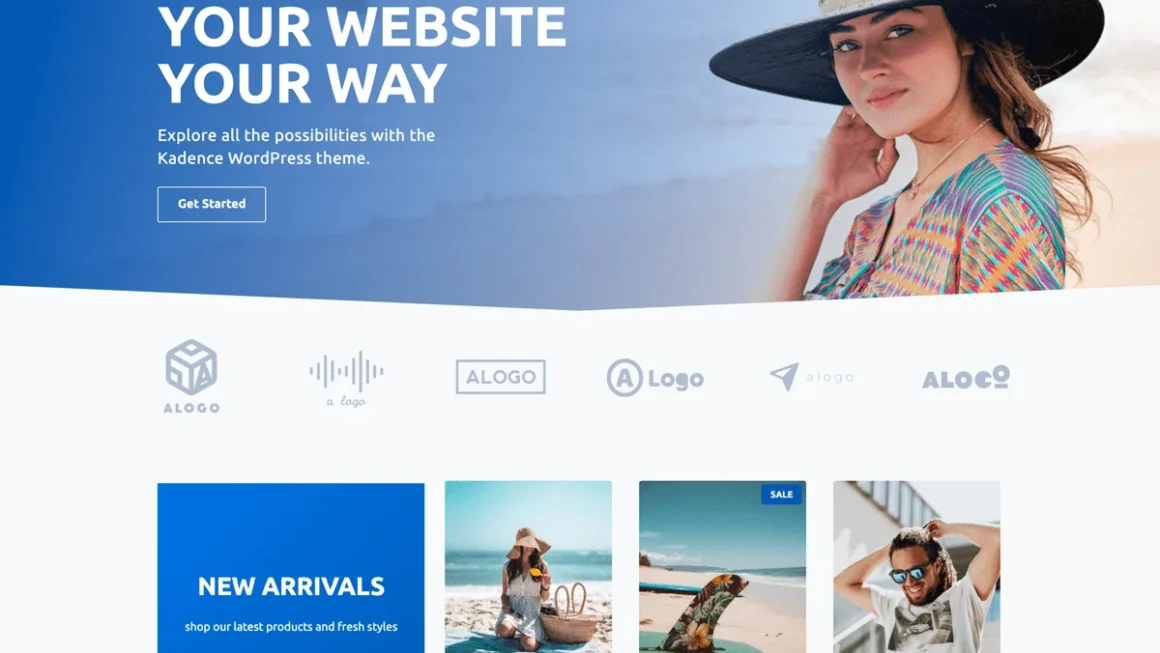
Powering Half a Million Sites: A Deep Dive into the Rise and Capabilities of the Kadence WordPress Theme
Introduction: The Evolution of WordPress Site Building In the vast ecosystem of content management systems, WordPress continues to hold a dominant position, powering a significant percentage of the global internet. Within this ecosystem, the choice of a theme acts as the foundational cornerstone for web design, performance, and user experience. Over the years, the community […]
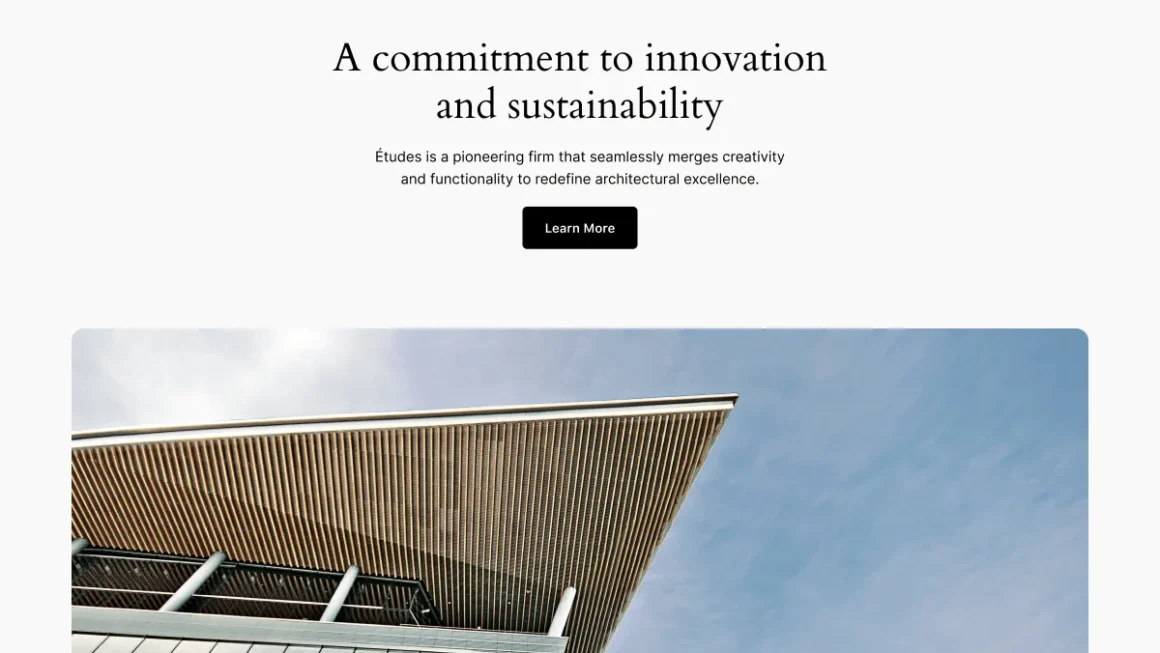
Inside Twenty Twenty-Four: How WordPress’s Flagship Theme Became a Versatile Powerhouse for Half a Million Sites
As the digital landscape continues to evolve at a blistering pace, the tools we use to build the web must adapt to meet the changing demands of creators, developers, and businesses alike. Entering the ecosystem with a mandate for absolute versatility, the Twenty Twenty-Four theme has rapidly ascended to become one of the most prominent […]
The Architect’s Toolkit: Mastering WordPress MU-Plugins for Cleaner, Faster, and More Secure Sites
For seasoned WordPress developers, the "functions.php" file is often both a sanctuary and a liability. It is the place where custom logic lives, yet it is notoriously fragile. One theme update, one accidental deletion, or a client’s unauthorized theme switch, and your meticulously crafted performance tweaks and security patches vanish into thin air. As of […]
Critical Security Advisory Issued for All in One SEO (AIOSEO) Plugin Impacting Over Two Million WordPress Sites
SAN FRANCISCO — A newly disclosed security advisory has brought to light two distinct vulnerabilities affecting the All in One SEO (AIOSEO) WordPress plugin, an enterprise-grade search engine optimization suite active on over two million websites globally. Security researchers have flagged both flaws as medium-severity issues that could allow unauthenticated malicious actors to execute arbitrary […]
Critical CSRF Vulnerability in Elementor Plugin Threatens Millions of WordPress Sites: Immediate Patch Issued
By Cybersecurity Desk Published: October 2023 The web security community has recently raised alarms regarding a severe security flaw discovered in Elementor, one of the most ubiquitous visual page builder plugins for WordPress. A high-severity Cross-Site Request Forgery (CSRF) vulnerability, affecting versions 4.3.0 and 4.3.1, has exposed millions of websites to potential full-site takeover risks. […]
Bridging AI and Content Management: How to Connect Claude to Self-Hosted WordPress Sites via Custom Connectors
As artificial intelligence continues to transition from a passive chat interface to an active, operational partner in digital workflows, integration capabilities have become the frontier of software development. For website administrators and developers, bridging the gap between large language models and content management systems has traditionally required complex, third-party automation tools like Zapier or custom-coded […]