SAN FRANCISCO — For decades, the digital economy has been built on a foundation of shifting sand: the human memory. From the early days of personal computing to modern cloud-native architectures, passwords have reigned supreme as the primary gatekeepers of our digital lives. Yet, they have long been recognized by security experts and engineers alike as a systemic vulnerability.
Users struggle to remember complex strings, frequently resort to dangerous habits like password reuse, and remain highly susceptible to sophisticated phishing campaigns. Simultaneously, service providers bear the operational weight of salting, hashing, rate-limiting, and managing endless password-reset cycles.
The tide, however, is finally turning. Industry-wide adoption of passkeys—powered by the W3C’s Web Authentication (WebAuthn) API—is rapidly accelerating. Rather than forcing users to memorize a shared secret, modern authentication leverages public-key cryptography tied to biometric sensors like fingerprints, facial recognition, or secure device PINs.
To demonstrate how engineering teams can transition away from legacy credentials, developers are increasingly adopting robust, modern tech stacks. A prime example is a full-stack architecture pairing a NestJS backend utilizing PostgreSQL with a Next.js frontend, streamlined by TypeScript libraries like SimpleWebAuthn.
This comprehensive report examines the structural flaws of password-based authentication, analyzes the mechanics of how passkeys solve them, and outlines the chronological implementation of a passwordless ecosystem.
The Anatomy of a Broken Model: Why Passwords Must Go
Before engineering a passwordless future, industry analysts emphasize the necessity of understanding the deep-seated flaws inherent in traditional authentication paradigms. For over thirty years, the fundamental security model has relied on a shared secret: something a user knows, which must be transmitted across networks and stored by services. Every single component of this model is fundamentally compromised.
1. The Perils of Phishing
Passwords are completely agnostic about where they are typed. If a malicious actor crafts a pixel-perfect replica of a banking or enterprise login portal, a targeted user will readily enter their credentials, blind to the fraudulent domain. While multi-factor authentication (MFA) via SMS or standard one-time password (OTP) applications provides a layer of defense, sophisticated adversary-in-the-middle (AiTM) phishing kits can easily intercept these codes in real time, rendering them insufficient against modern threats.
2. Credential Stuffing and Password Reuse
Human cognitive limits prevent individuals from memorizing dozens—let alone hundreds—of unique, high-entropy passwords. Consequently, users inevitably reuse the same combinations across multiple platforms. Cybercriminals weaponize this behavior through automated "credential stuffing" attacks. A data breach at a low-security e-commerce site routinely yields credentials that attackers immediately test against high-value financial, corporate, and email accounts.
3. The Burden of Data Breaches
Under the password paradigm, database security is a high-stakes tightrope walk. Even when developers implement best-practice salting and robust hashing algorithms (such as Argon2 or bcrypt), compromised databases remain targets for offline brute-force attacks. The responsibility of securing and protecting raw or hashed secrets rests entirely on the service provider, transforming minor infrastructure leaks into catastrophic privacy disasters.
4. Privacy Violations and Credential Fatigue
Because users pass identical credentials across multiple services, malicious actors can correlate breaches across disparate platforms, mapping comprehensive behavioral profiles of individuals. Furthermore, the relentless imposition of complex password policies—forcing frequent resets, specialized character requirements, and obscure security questions—leads directly to "credential fatigue." This psychological exhaustion drives users toward predictable patterns, such as appending sequential numbers or writing sticky notes to attach to their monitors.
Chronology of Modern Authentication: From Cryptographic Standards to Passkeys
The journey toward modern passwordless infrastructure is rooted in decades of cryptographic research, evolving from enterprise hardware tokens to ubiquitous software standards.
- Early 2000s (Hardware Tokens): Enterprises relied heavily on specialized hardware tokens, such as RSA SecurID, which generated time-based codes. While secure, these devices were expensive, cumbersome, and impractical for consumer-facing web applications.
- 2012 (FIDO Alliance Formation): Recognizing that passwords were a universal bottleneck for commerce and security, industry leaders formed the Fast IDentity Online (FIDO) Alliance to create open, royalty-free authentication standards.
- 2019 (WebAuthn W3C Recommendation): The World Wide Web Consortium (W3C) officially adopted WebAuthn as a web standard. This breakthrough allowed developers to integrate cryptographic public-key authentication directly into web browsers without requiring proprietary browser plugins.
- 2022–Present (The "Passkey" Revolution): Major technology ecosystems—including Apple, Google, and Microsoft—interoperably adopted WebAuthn credentials under the consumer-friendly term "passkeys." Passkeys introduced seamless cloud synchronization, enabling credentials to securely back up to device ecosystems (like iCloud Keychain and Google Password Manager) and operate across multiple personal devices via secure QR-code handshakes.
Supporting Data: How Passkeys Neutralize Threats
The structural shift of passkeys relies on changing where trust resides. Instead of trusting the user’s memory and vigilance against fraudulent sites, trust is delegated to the operating system and the browser, which enforce strict cryptographic domain binding.
| Security Threat | Traditional Password Model | Passkey / WebAuthn Solution |
|---|---|---|
| Phishing Attacks | High vulnerability; credentials work on any domain that requests them. | Zero vulnerability; the browser cryptographically binds the key to the exact domain origin. |
| Credential Reuse | Widespread; users utilize the same password across multiple platforms. | Impossible; every passkey is a unique, generated key pair specific to a single site. |
| Data Breaches | High risk; leaked password hashes can be cracked offline. | Low risk; the server stores only a public key, which is useless to attackers without the private key. |
| User Privacy | Low; shared secrets allow third-party correlation across leaked databases. | High; biometric data never leaves the local device, and keys remain entirely isolated per domain. |
| Credential Fatigue | Severe; users suffer from cognitive overload, leading to weak passwords. | Eliminated; authentication relies on standard device biometrics used multiple times daily. |
Implementing a Modern Passwordless Stack: Next.js, NestJS, and SimpleWebAuthn
To demonstrate how modern engineering teams implement this architecture, developers can construct a decoupled full-stack application. The backend utilizes a NestJS framework integrated with PostgreSQL via TypeORM, while the frontend runs on a Next.js application utilizing the App Router and Tailwind CSS. Cryptographic parsing is managed via the SimpleWebAuthn TypeScript library.
1. Backend Architecture (NestJS & PostgreSQL)
The backend infrastructure is split primarily across two entities: a User entity containing account metadata and a unique webauthnId (user handle), and an Authenticator entity holding cryptographic public keys, signature counters, and device transport types.
During the registration phase, the server generates cryptographic options using generateRegistrationOptions, enforcing discoverable credentials (residentKey: 'required') and strict user verification (userVerification: 'required').
// Example snippet from NestJS AuthService registration option generation
const options = await generateRegistrationOptions(
  rpName: this.rpName,
  rpID: this.rpID,
  userID: Buffer.from(user.webauthnId, 'base64url'),
  userName: user.email,
  attestationType: 'none',
  authenticatorSelection:
    residentKey: 'required',
    userVerification: 'required',
  ,
);
Once the client responds, the server calls verifyRegistrationResponse, ensuring that the expected challenge matches the database record and validating that the origin and relying party ID (RP ID) align precisely with development or production environments.
2. Frontend Integration (Next.js & Browser APIs)
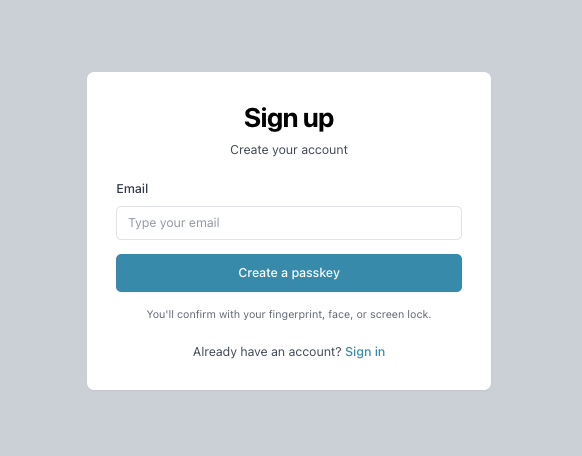
On the client side, the integration is remarkably concise. Utilizing @simplewebauthn/browser, the Next.js application fetches initialization options from the NestJS API and hands them directly to the browser’s native capabilities.
// Example snippet from Next.js Sign-Up component
const handleRegistration = async (e: React.FormEvent) =>
  e.preventDefault();
  try
    const options = await webAuthnApi.getRegistrationOptions(email);
    const regResult = await startRegistration( optionsJSON: options );
    const verificationResult = await webAuthnApi.verifyRegistration(email, regResult);

    if (verificationResult.verified)
      router.push('/welcome');

   catch (err)
    console.error('Registration failed:', err);

;
When startRegistration or startAuthentication is invoked, the browser instantly triggers the host operating system’s native biometric prompt—whether that is Touch ID on macOS, Face ID on iOS, Windows Hello, or an Android fingerprint sensor.
Critical Security Considerations and Pitfalls
While passkeys offer unprecedented security guarantees, backend implementation flaws can introduce critical vulnerabilities. Engineers deploying WebAuthn systems must guard against several subtle edge cases:
- Challange Reuse Prevention: Challenges generated by the server must be strictly single-use. Developers must clear challenges explicitly using
nullrather thanundefined, as Object-Relational Mappings (ORMs) like TypeORM may silently ignoreundefinedupdates, leaving stale challenges vulnerable to replay attacks. - Strict Authenticator Lookups: During authentication verification, developers must never query authenticators solely by their credential ID. Attackers can register their own passkeys and attempt to sign challenges intended for other users. Queries must always enforce a composite lookup combining both the credential ID and the validated user ID.
- Preventing Account Association Hijacking: Public registration endpoints must explicitly check whether an account already exists. Allowing an unauthenticated user to append a new passkey to an existing email record enables malicious actors to hijack accounts by simply registering their own biometrics against a victim’s email address.
Industry Implications and Future Outlook
The mass migration toward passkeys represents a watershed moment for cybersecurity and user experience. For enterprises, widespread passkey deployment drastically reduces IT support overhead associated with password resets, which frequently account for a significant percentage of help desk tickets. Furthermore, by effectively eliminating credential-based attack vectors, organizations drastically lower their risk profile against automated botnets and targeted phishing campaigns.
Major technology platforms have already begun aggressively deprecating passwords in favor of passkeys as default account settings. As browser support matures and cross-device synchronization protocols become universally standardized, the digital landscape is approaching a tipping point where passwords will be viewed as an archaic legacy technology—much like cleartext HTTP or unencrypted telephone lines.
For software engineers, adopting stacks that seamlessly integrate WebAuthn—such as NestJS, Next.js, and SimpleWebAuthn—is no longer an experimental exercise. It is rapidly becoming the baseline standard for secure, resilient, and user-friendly web application architecture.