By Global Cybersecurity Desk
Published: October 2026
Introduction: The Invisible Threat in Your Browser
That routine digital advertisement flashing on your screen—promoting everyday consumer goods like wireless earbuds, a drone, or a bubble gum-scented car air freshener—may be operating as an advanced digital Trojan horse.
In a groundbreaking and deeply unsettling revelation, researchers at The Citizen Lab at the University of Toronto have exposed a sophisticated cyber-surveillance pipeline. Dubbed "AdFection," this campaign leverages the multi-billion-dollar programmatic advertising ecosystem to deliver zero-click mercenary spyware directly to unsuspecting internet users. Unlike traditional malware that relies on phishing emails or malicious links, zero-click attacks require no user interaction whatsoever. Simply rendering the ad on a webpage or mobile application is enough to quietly compromise a target’s device.
The findings expose a structural vulnerability at the heart of the modern internet. Major tech platforms and ad-exchange networks—unwittingly manipulated by a shadowy Israeli firm masquerading as a legitimate digital marketing agency—have been used to facilitate state-grade surveillance on a global scale.
Main Facts: The Anatomy of AdFection
The Citizen Lab’s technical disclosure, published alongside companion investigations from ad-security firm Confiant, details an operation where standard digital advertising serves as the delivery vector for some of the world’s most aggressive commercial spyware suites.
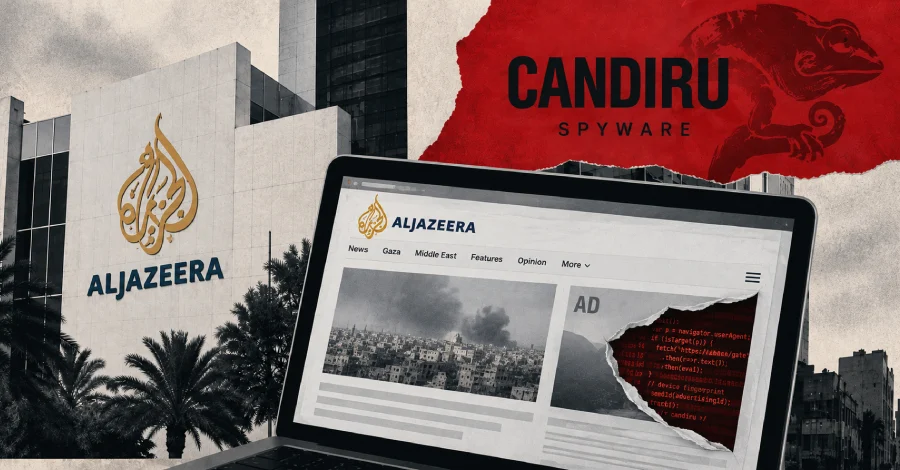
- The Primary Perpetrator: Discover-Tech, an Israel-registered firm, presented itself to the ad tech industry as a standard advertising vendor. In reality, researchers concluded that Discover-Tech functions as a core logistical hub for multiple mercenary spyware vendors, most notably the infamous Candiru.
- The Scale of the Attack: Between March and June of this year alone, malicious ads linked to Discover-Tech were served across more than 120,000 websites and 70,000 mobile applications.
- High-Profile Targets: The campaign successfully compromised or targeted devices connected to highly sensitive networks worldwide. Among the confirmed victims are journalists and personnel at the prominent media outlet Al Jazeera, alongside incursions or detections near networks belonging to the U.S. Department of Defense, NATO, the International Atomic Energy Agency (IAEA), and international cybersecurity agencies.
- The Mechanics of Controlium: Discover-Tech operates a proprietary platform called Controlium. This system enables its mercenary partners to instantly de-anonymize targets, gather device fingerprints, and trigger automated malware infections the exact microsecond an advertisement is rendered on a user’s screen.
- The "Dark Cartographer" Nexus: Researchers also identified a secondary, highly enigmatic threat actor labeled DARK CARTOGRAPHER. This group utilizes Discover-Tech’s underlying infrastructure to exploit telecommunications vulnerabilities worldwide, linking device advertising IDs directly to real-world phone numbers to execute mass, automated de-anonymization of internet users.
Chronology of an Undetected Threat
The emergence of AdFection did not happen overnight; it represents the maturation of years of quiet, systemic exploitation of the digital ad-bidding market.
- 2019: Activities tied to the "Dark Cartographer" ecosystem—involving Discover-Tech alongside other undisclosed entities, including an unnamed U.S. government intelligence contractor—begin taking shape. This marks the foundational development of weaponized ad-tech infrastructure.
- 2020: Discover-Tech is officially registered as a corporate entity. It successfully maneuvers through vetting processes to secure spots on "certified" and "approved" vendor registries maintained by major tech conglomerates, including Google and the Interactive Advertising Bureau (IAB) Europe.
- 2024: Discover-Tech is confirmed to be actively facilitating mercenary spyware distribution on a commercial scale, operating undetected beneath the regulatory and technical radar of the digital advertising industry.
- March–June 2026: Intensive monitoring by The Citizen Lab and Confiant captures Discover-Tech ads sweeping through global digital real estate, appearing on upwards of 120,000 websites and 70,000 mobile apps.
- October 2026: The Citizen Lab publicly details the AdFection findings. In response to the disclosures, major tech players move swiftly to revoke Discover-Tech’s accreditations and platform access.
Supporting Data and Technical Realities
To understand the severity of AdFection, one must look at how the digital advertising ecosystem—known commonly as "adtech"—operates. Programmatic advertising relies on lightning-fast auctions where billions of ad impressions are bought and sold in milliseconds. Billions of tracking pixels, scripts, and content delivery networks (CDNs) load simultaneously every time a user opens a page.
Mercenary spyware vendors recognized that this high-velocity, high-trust environment was the ideal camouflage.
Key Technical Findings:
- Zero-Click Mechanics: When a user loads a webpage containing a poisoned ad slot, the creative asset executes code that evaluates the device’s environment. If the device matches the profile of a high-value target, the underlying infrastructure interacts with command-and-control servers—such as those run by Candiru—to silently push exploits.
- Beyond Candiru: While Candiru is the most prominent partner tied to the leaks, researchers discovered deep architectural connections between Discover-Tech and other offensive security players, including mercenary hacking firm Bindecy and market intelligence outfit Intelos.
- The Al Jazeera Breaches: With high confidence, researchers linked Discover-Tech ad payloads to zero-click infections targeting at least 45 individual devices belonging to personnel at Al Jazeera. Once installed, spyware like Candiru grants total remote access: reading encrypted messages, hijacking front- and rear-facing cameras, recording audio via the microphone, and exfiltrating localized documents.
- Mass Vulnerability Exploitation: Confiant’s telemetry revealed that the ads did not merely target niche dissidents; they cast a massive net that brushed against military, diplomatic, and regulatory networks across North America, Europe, and the Middle East.
Official Responses and Industry Fallout
The fallout from The Citizen Lab’s report has triggered immediate, defensive restructuring among industry giants who historically treated ad-fraud primarily as a financial nuisance rather than a national security threat.
- Google’s Action: Following the coordinated disclosure, Google removed Discover-Tech from its certified vendor lists and terminated the company’s access to all Google ad-bidding and monetization platforms.
- IAB Europe: The Interactive Advertising Bureau Europe similarly expelled Discover-Tech from its Global Vendor List (GVL), aiming to cut off the firm’s programmatic reach.
- The Accused Remain Silent: Despite repeated inquiries and formal outreach letters sent by The Citizen Lab prior to publication, representatives from Discover-Tech, Candiru, Bindecy, and Intelos declined to provide comment.
Industry leaders pulled no punches when assessing the systemic nature of the failure. Jerome Dangu, chief technology officer and co-founder of Confiant, noted that the digital advertising sector has spent decades optimizing defenses strictly against financial cybercriminals, scams, and low-level malware.
"The industry has optimized against cyber criminals, scams and malware for profit that targets people for extracting money, but not for surveillance," Dangu stated. "The adtech industry, the digital advertising industry, has a lot of rethinking to do to reconsider how they approach these threats of surveillance and the responsibilities that they have with the data that they collect and how it might be abused."
Wolfie Cristl, senior researcher at The Citizen Lab, went a step further, describing the multi-year oversight as "disastrous" and calling for immediate government intervention.
"Digital advertising is broken. The way the online advertising ecosystem works today is a security threat for states, the private sector, civil society and everyone else alike," Cristl said. "Cybersecurity agencies, regulators and lawmakers in the U.S., Europe and other regions must urgently step in. They must investigate the involved companies and fix the systemic risks that enable malicious ad targeting."
Implications: A Crisis for Regulators and National Security
The exposure of AdFection shatters the long-held illusion that digital surveillance tools require complex, bespoke state-sponsored spear-phishing campaigns to reach high-value targets. By subverting standard commercial ad delivery, spyware operators have weaponized the infrastructure of the internet itself.
1. Regulatory Blind Spots
Traditional privacy regulations—such as Europe’s GDPR or various state-level U.S. privacy laws—focus heavily on data collection, user consent, and commercial monetization. They were fundamentally not designed to address commercial spyware vendors leveraging legitimate ad-bidding networks to execute code on government and civil society devices. Regulators now face mounting pressure to classify adtech security lapses as critical national security vulnerabilities.
2. The Blurred Lines of Intelligence Contractors
One of the most alarming footnotes in The Citizen Lab’s preliminary findings is the direct overlap discovered between DARK CARTOGRAPHER’s infrastructure, mercenary ad-tech vendors, and an unnamed U.S. government intelligence contractor. The intersection of private commercial surveillance entities and Western intelligence supply chains complicates diplomatic and legal efforts to crack down on the mercenary spyware market. While Washington has attempted to sanction firms like Intelos and the broader Intellexa consortium, the porous nature of intelligence contracting frequently allows grey-market cyber capabilities to persist through shifting corporate shells.
3. The End of Passive Browsing Safety
For the average internet user, media organization, and government employee, AdFection proves that standard hygiene practices—such as avoiding suspicious links or refusing to open strange email attachments—are no longer sufficient protection. When simply loading a news portal or checking the weather on a mobile app can expose a device to zero-click spyware via a standard advertisement, the foundational trust of the web is severely undermined.
Conclusion
The unveiling of the AdFection campaign marks a dark milestone in the evolution of digital espionage. It demonstrates that the multi-trillion-dollar online advertising ecosystem has become a high-efficiency pipeline for authoritarian and commercial surveillance alike.
As lawmakers in Washington and Brussels digest the implications of the report, the mandate for the technology sector is clear. Programmatic advertising can no longer prioritize sheer velocity and unvetted reach over basic network integrity. Until stringent, cryptographic-level vetting is mandated across global ad-exchanges, every banner ad, video pre-roll, and mobile popup will remain a potential vector for invisible, silent occupation.