By Tech Wire Services
Published: October 23, 2026
Main Facts
The Fedora Project has officially announced a postponement of the highly anticipated Fedora 45 release, pushing its public rollout to November 3, 2026. The decision stems from the community’s rigorous "blocker" vetting process, which identifies critical bugs, regressions, and security vulnerabilities that must be resolved prior to a stable deployment.
Chief among the four active release blockers halting Fedora 45 is a widespread security concern involving compromised website certificates issued by certificate authority eMudhra. The eMudhra incident exposed cryptographic private keys that were trivially easy to crack—with one notable instance relying simply on the number "4." Because current Fedora builds trust these vulnerable intermediate certificates, developers and community members argued that pushing a release without patching this oversight would leave end-users exposed.
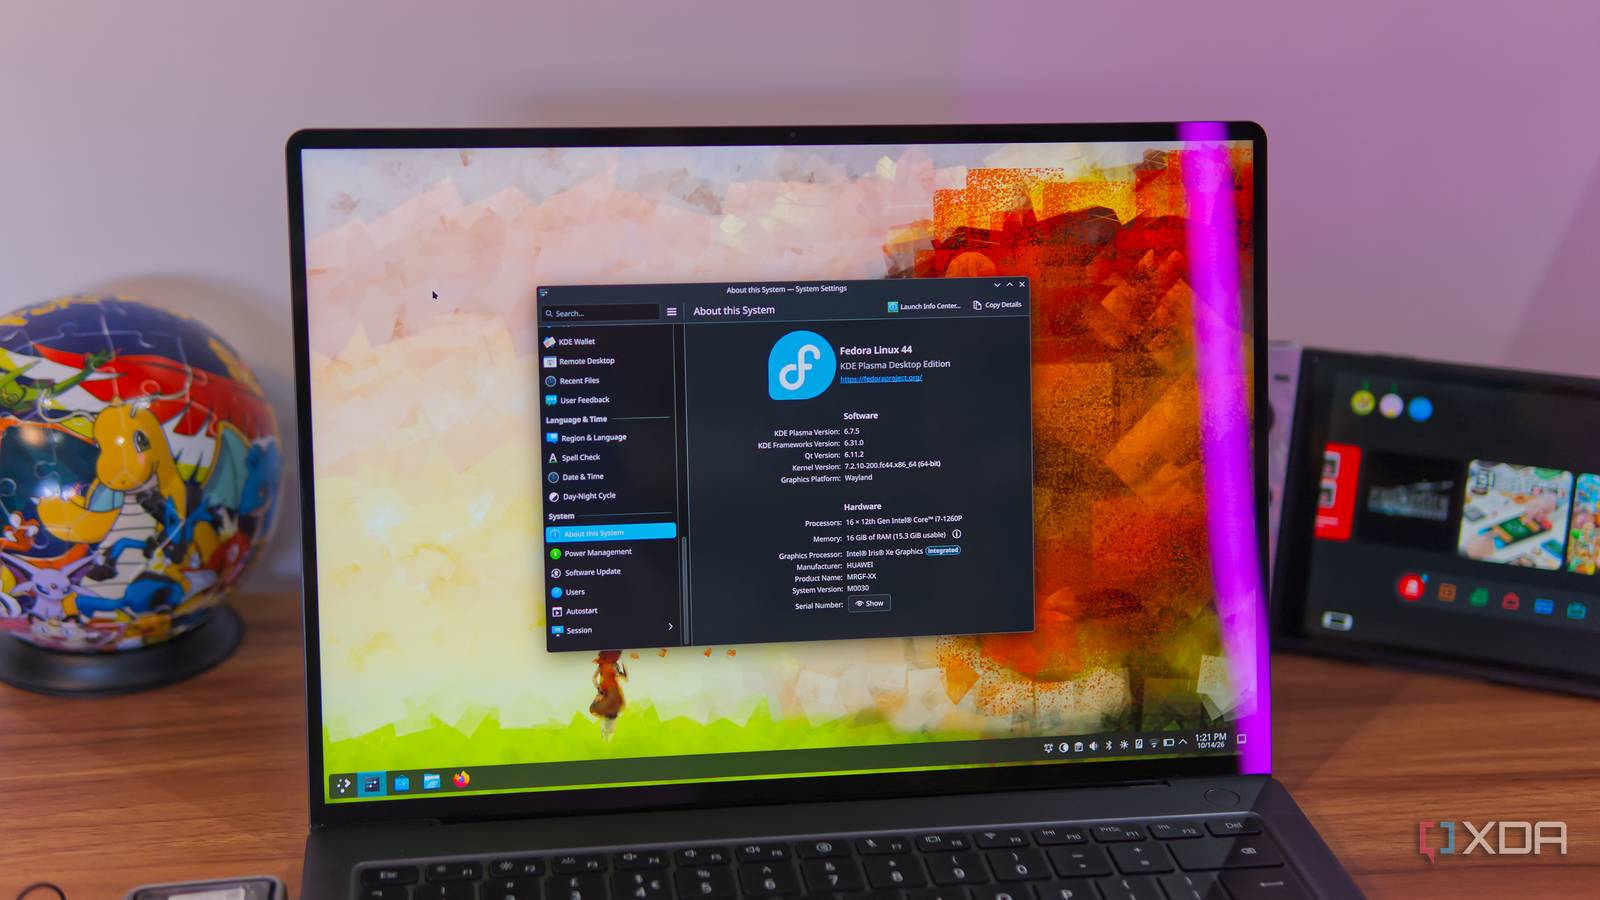
Alongside the cryptographic certificate flaw, the Fedora engineering team must clear three additional technical hurdles: a failure in Logical Volume Manager (LVM) autoactivation following upgrades to Fedora 45, the KDE Plasma Discover package manager pulling outdated RPM packages intended for Fedora 44, and a boot-failure bug impacting Stratis encrypted storage pools.
Chronology of Events
The path toward the Fedora 45 delay unfolded over several weeks of routine pre-release testing, culminating in emergency discussions among developers and quality assurance teams:
- Early October 2026: The broader cybersecurity community uncovers a profound cryptographic flaw affecting digital certificates issued by eMudhra. Independent researchers reveal that the private keys associated with specific intermediate certificates lack adequate entropy, making them susceptible to immediate factorization and exploitation.
- Mid-October 2026: As independent vulnerability trackers—such as the diagnostic portal eMudhra We Have A Problem—confirm that numerous operating systems and software distributions automatically trust these compromised certificates, developers audit mainstream Linux distributions.
- Shortly Before the Scheduled Launch: During the final pre-release Go/No-Go meeting managed by the Fedora QA and engineering steering committees, community members file four official "release blockers." One of these formal bugs directly cites the eMudhra certificate crisis, noting that Fedora systems still accept the vulnerable intermediates and lack immediate updates in the Bodhi update system.
- October 22–23, 2026: Recognizing the severity of the certificate flaw alongside persistent infrastructure bugs—including LVM autoactivation failures and Stratis pool boot crashes—the Fedora community votes unanimously for a "No-Go" status, officially rescheduling the release target for November 3, 2026.
Supporting Data and Technical Breakdown
The decision to hold back an operating system release is never taken lightly within the open-source community, particularly for a distribution as prominent as Fedora, which serves as both an innovation pipeline for Red Hat Enterprise Linux (RHEL) and a daily driver for millions of developers and enthusiasts.
The technical weight of the four active blockers is detailed below:
1. The eMudhra Certificate Vulnerability (Bugzilla #2556376)
Cryptographic certificates rely on the mathematical complexity of large prime numbers to secure web traffic, software updates, and encrypted communications. The eMudhra incident exposed a severe breakdown in key generation protocols. According to security reports, certain private keys utilized by the authority were generated with abysmal entropy, resulting in keys that could be factored instantaneously.
When an operating system trusts an intermediate certificate authority with compromised keys, malicious actors can theoretically execute sophisticated man-in-the-middle (MitM) attacks, spoof trusted web domains, or compromise the integrity of software repositories. The Fedora blocker documentation emphasizes that testing tools confirm fresh Fedora environments are inherently trusting these vulnerable intermediates, demanding an urgent cryptographic revocation update before general availability.
2. LVM Autoactivation Regressions
Logical Volume Manager (LVM) is a staple storage management tool in enterprise and advanced Linux environments. Testing revealed that systems upgrading directly to Fedora 45 experience catastrophic failures in LVM autoactivation. Without proper volume mounting during the early boot sequence, users risk encountering unbootable systems or missing partition tables upon restarting their machines.
3. KDE Plasma Discover RPM Mismatch
For users favoring the KDE Plasma desktop environment, software management is typically handled through the Discover graphical package manager. QA testing flagged a regression where Plasma Discover attempts to fetch and install outdated RPM packages intended for Fedora 44 rather than targeting the updated package repositories of Fedora 45, which threatens to destabilize user software stacks and trigger dependency conflicts.
4. Stratis Encrypted Storage Pool Failures
Stratis provides advanced storage management features—such as thin provisioning, snapshots, and encryption—built on top of device mapper and XFS. A critical bug identified in the pre-release phase causes Stratis-managed encrypted pools to fail during system initialization. For users relying on full-disk encryption and automated pool management, this bug represents a total showstopper.
Official Responses and Community Reactions
Reactions from the Linux community have been overwhelmingly supportive of the delay, prioritizing system integrity and security over rigid adherence to calendar deadlines.
In public mailing lists and bug-tracking threads, Fedora developers emphasized the philosophy of the "Blocker Bug Process." The framework exists precisely to prevent compromised security postures from reaching the public. By catching the eMudhra vulnerability before the installation media was signed and mirrored globally, the Fedora Project averted a post-release scramble that would have forced emergency patches on millions of active endpoints.
Security researchers tracking the eMudhra We Have A Problem initiative have praised Linux distributions taking swift action. While major commercial operating systems often push out telemetry-driven background patches to handle certificate trust stores, community-driven distributions like Fedora require explicit package updates rolled into their core trust store packages (such as ca-certificates), necessitating a coordinated rebuild of the release candidate images.
Implications for Users, Developers, and the Enterprise Ecosystem
The temporary postponement of Fedora 45 carries several noteworthy implications for the broader software development landscape:
- Heightened Scrutiny on Certificate Authorities: The eMudhra incident highlights ongoing vulnerabilities in the Public Key Infrastructure (PKI) ecosystem. Even as automated validation protocols improve, human error or flawed hardware security modules (HSMs) at certificate authorities can introduce systemic risks that trickle down into operating system trust stores.
- The Value of Rigorous QA in Linux: Incidents like this validate the deliberate pace of open-source quality assurance. While users eager to test the latest kernel versions, GNOME or KDE desktop environments, and toolchains must wait until November 3, the delay ensures that foundational storage (Stratis, LVM) and security layers remain uncompromised.
- Upstream Stability for RHEL: Because Fedora serves as the foundational testing ground for Red Hat Enterprise Linux, catching regressions in storage management and cryptographic handling helps insulate downstream enterprise customers from critical Day-0 vulnerabilities.
As the Fedora development team races to patch the certificate trust stores, resolve package manager routing issues, and squash storage bugs, the November 3 launch date stands as the next critical milestone for one of the Linux world’s most influential distributions.