

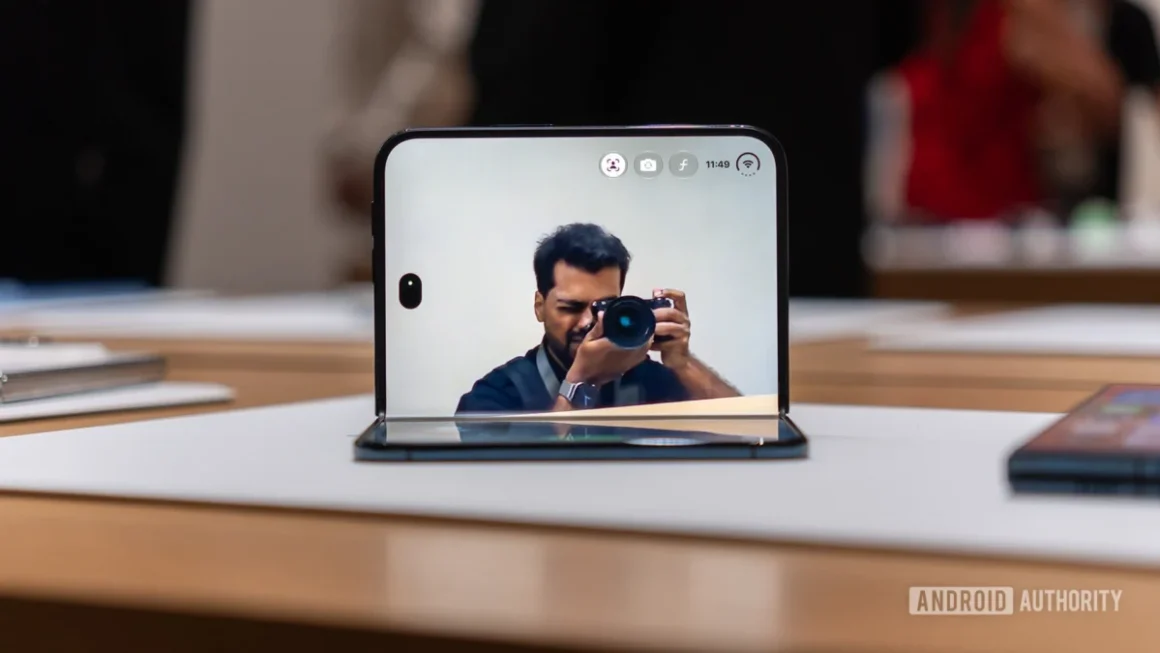
The long-awaited arrival of Apple’s first foray into the foldable smartphone market, the iPhone Duo, was intended to be a watershed moment in mobile technology. Scheduled for a global release on October 23, the device was met with record-breaking anticipation, intense media scrutiny, and a price tag that positions it firmly in the ultra-premium tier […]
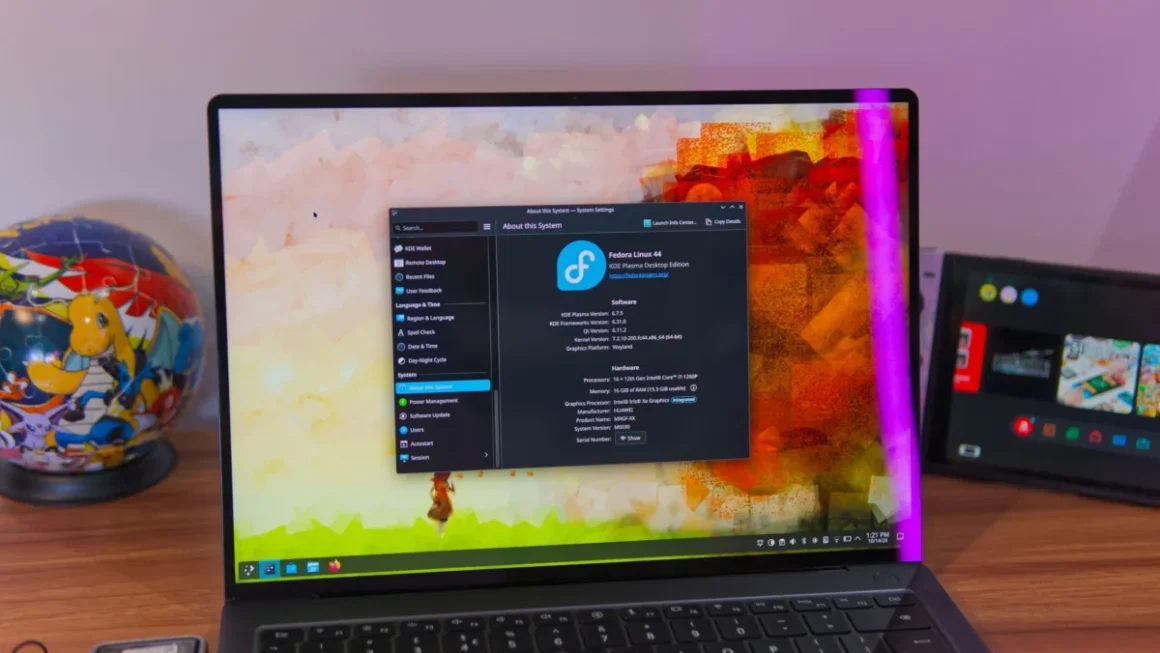
Fedora 45 Release Delayed to November Following Critical eMudhra Certificate Flaw and System Blockers
By Tech Wire Services Published: October 23, 2026 Main Facts The Fedora Project has officially announced a postponement of the highly anticipated Fedora 45 release, pushing its public rollout to November 3, 2026. The decision stems from the community’s rigorous "blocker" vetting process, which identifies critical bugs, regressions, and security vulnerabilities that must be resolved […]
Indian Certificate Authority eMudhra Exits Global SSL/TLS Business After Catastrophic Cryptographic Flaw Exposed Private Keys
NEW DELHI — In an extraordinary collapse of digital trust that has sent shockwaves through the global cybersecurity community, Indian certificate authority (CA) eMudhra announced Thursday that it will completely cease issuing global SSL/TLS certificates. The decision follows a catastrophic security failure in which researchers discovered that the private cryptographic keys securing eight of the […]
Critical Privacy Vulnerability in Signal: Understanding the RingRTC “Ghost Call” Flaw
In an era where digital privacy is the cornerstone of secure communication, the discovery of a significant vulnerability in the Signal messaging app has sent shockwaves through the cybersecurity community. Signal, widely regarded as the gold standard for encrypted communication, recently faced a serious challenge to its reputation for total privacy. A newly disclosed flaw, […]
Decoding Generative Search: Is Your Content Suffering from an Authority Gap or a Structural Flaw?
October 19, 2026 — 6 min read As the digital marketing landscape undergoes a massive transformation, search engine optimization (SEO) is no longer solely about traditional search engine result pages (SERPs). We have officially entered the era of Generative Engine Optimization (GEO). As brands fight for visibility within AI-generated summaries, conversational chatbots, and synthesized knowledge […]
Critical "PwnEscape" Linux Kernel Flaw Exposes Cloud Sandboxes to Memory Leaks and Host Takeovers
SAN FRANCISCO — A newly disclosed, highly critical vulnerability in the Linux kernel has sent ripples through the cloud computing industry. Tracked as CVE-2026-99999 and colloquially dubbed "PwnEscape," the security loophole allows code running inside an isolated virtual machine (VM) to bypass its boundaries and read host computer memory. The flaw was discovered during a […]
The Unraveling of ‘Rey’: How a Teenage Hacker, a Boeing Divestment, and an Oracle Flaw Brought Down the New Face of ShinyHunters
AMMAN / WASHINGTON / AMSTERDAM — In the murky, high-stakes underworld of international cybercrime, the moniker "ShinyHunters" has long evoked terror. Responsible for billions of stolen records and catastrophic data breaches dating back to 2019, the brand became synonymous with ruthless data theft, extortion, and psychological harassment. But as law enforcement agencies closed in, the […]
Critical Flaw in Cisco Secure Email Gateway Under Active Exploitation: Root-Level Access Vulnerability Threatens Enterprise Networks
By Global Cybersecurity Desk Published: October 2026 Main Facts: The Zero-Day Crisis Unfolding at Cisco Cisco Systems has issued an urgent security advisory warning that threat actors are actively exploiting a critical, unauthenticated remote code execution vulnerability in the Cisco Secure Email Gateway. Tracked as CVE-2026-76519 and carrying a maximum severity CVSS score of 9.8 […]
GitHub Tightens npm Security Following "SlugFest" Flaw Discovery
SAN FRANCISCO — In a swift move to patch a critical software supply chain vulnerability, GitHub has announced that unvalidated npm trusted publishing configurations will now automatically expire 48 hours after creation. The update comes in direct response to vulnerability research conducted by Bloom Security, which uncovered a systemic architectural flaw dubbed "SlugFest." This loophole […]
Critical Security Alert: Active Exploitation of Atlassian Data Center Flaw CVE-2026-21589
In a stark reminder of the fragile nature of enterprise software security, a critical vulnerability within Atlassian’s Data Center product suite has triggered a global scramble among IT security teams. Designated as CVE-2026-21589, this arbitrary file access flaw carries a CVSS severity score of 9.3, placing it firmly in the "Critical" category. The vulnerability, which […]