










In a stark reminder of the fragile nature of enterprise software security, a critical vulnerability within Atlassian’s Data Center product suite has triggered a global scramble among IT security teams. Designated as CVE-2026-21589, this arbitrary file access flaw carries a CVSS severity score of 9.3, placing it firmly in the "Critical" category. The vulnerability, which […]
Critical Security Alert: Atlassian Data Center Flaw Under Active Exploitation Following Disclosure
The cybersecurity landscape has been thrust into a state of high alert following the discovery of a critical arbitrary file access vulnerability, cataloged as CVE-2026-21589, affecting a wide array of Atlassian’s self-managed Data Center products. Within hours of the release of technical analysis and proof-of-concept (PoC) material by security researchers, threat actors have already begun […]
Hello Biz Surpasses 100,000 Active Installations: A Deep Dive into WordPress’s Rising Hybrid Theme for Elementor
SAN FRANCISCO — In the ever-evolving landscape of content management systems and web design toolkits, finding a harmonious balance between beginner-friendly onboarding and advanced customization has long been the holy grail for developers. Enter Hello Biz, a free, hybrid WordPress theme specifically engineered to integrate seamlessly with the ubiquitous Elementor page builder. Reaching a monumental […]
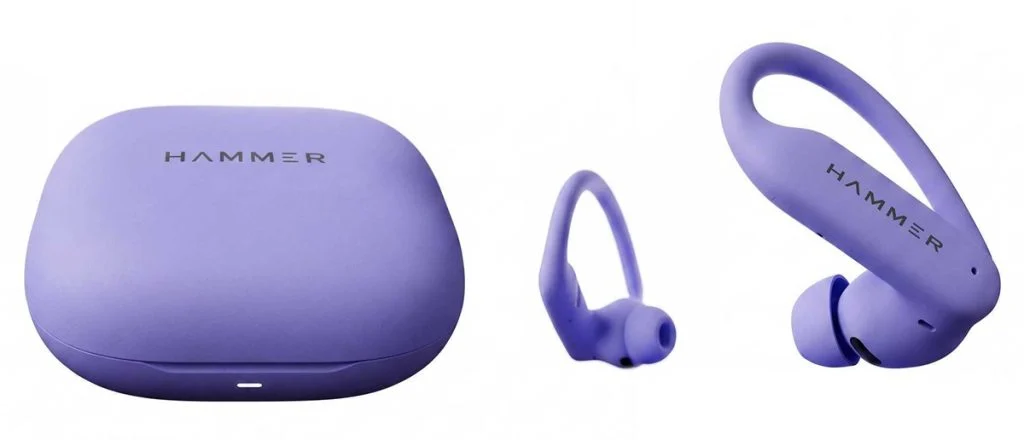
HAMMER Redefines Active Audio: A Deep Dive into the New KO2 Sports TWS Earbuds
In an increasingly crowded audio market, lifestyle and sports-centric consumer electronics brand HAMMER has taken a bold step forward. With the official launch of the KO2 Sports TWS Earbuds, the company is aiming to bridge the gap between high-performance athletic gear and immersive personal audio. Priced at an aggressive entry-level point of Rs. 1,299, the […]
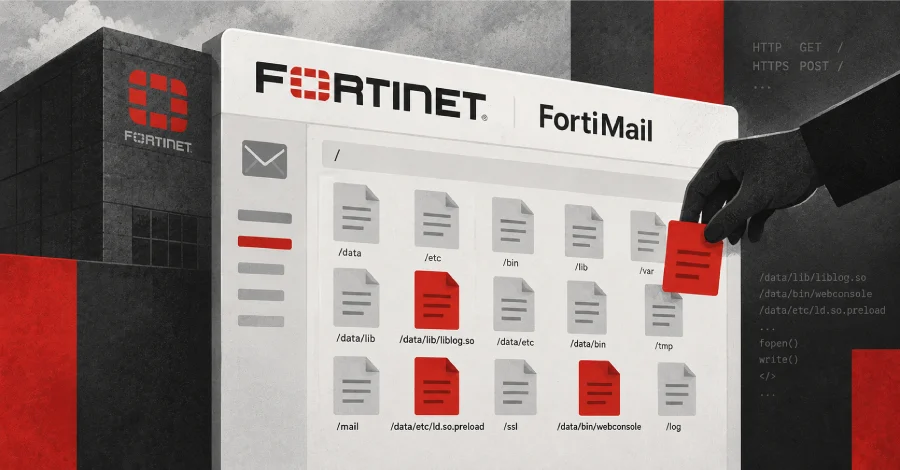
Critical Fortinet FortiMail Flaw Added to CISA KEV Catalog Amid Active In-the-Wild Exploitation
By Ravie Lakshmanan | October 02, 2026 Vulnerability / Enterprise Security Main Facts The United States Cybersecurity and Infrastructure Security Agency (CISA) has officially added a critical security vulnerability impacting Fortinet’s FortiMail secure email gateway to its heavily watched Known Exploited Vulnerabilities (KEV) catalog. The inclusion follows mounting intelligence and direct telemetry confirming that threat […]
Hello Biz Reaches 100,000 Active Installations: How This Hybrid WordPress Theme is Reshaping Business Web Design
In the fast-paced ecosystem of WordPress development, finding a theme that strikes the ideal balance between beginner-friendly simplicity and professional-grade capability has historically been a challenge. Web creators, startup founders, and agency developers often find themselves choosing between rigid, out-of-the-box templates that offer little room for customization or complex blank-canvas frameworks that demand extensive coding […]
Cisco Confronts Back-to-Back Crises: Maximum-Severity Zero-Day Discovered in Identity Services Engine Amid Active Exploitation
SAN JOSE, California — In a brutal week for enterprise network defenders, networking giant Cisco Systems has disclosed its second actively exploited zero-day vulnerability in as many days. The latest flaw, carrying a maximum-severity rating of 10, targets the Cisco Identity Services Engine (ISE)—the critical backbone many organizations rely on to enforce network access policies, […]