

By Editorial Staff October 21, 2026 In a significant development for the global web infrastructure, the PHP development team issued an emergency security release today, October 21, 2026, addressing two critical vulnerabilities that threaten the integrity of millions of websites worldwide. These flaws, which allow for Remote Code Execution (RCE), represent a top-tier security risk. […]
The PHP "Code-Red": How AI-Discovered Vulnerabilities Brought the Global Web to a Standstill
In a staggering development that has reverberated through the corridors of government and the boardrooms of global corporations, two critical vulnerabilities in the PHP programming language—the backbone of the modern internet—have forced a worldwide security scramble. The flaws, which threaten to expose the file systems and databases of nearly 70% of the web, represent a […]
Critical "php2shell" Vulnerabilities Trigger Global Emergency Patching as AI-Driven Exploits Redefine Cybersecurity
By CyberScoop Reporting Desk Updated October 21, 2026 Main Facts The global digital infrastructure is currently scrambling to neutralize a pair of catastrophic remote code execution (RCE) vulnerabilities discovered in PHP, one of the foundational programming languages of the modern web. Formally cataloged as CVE-2026-109618 and CVE-2026-109619, both security flaws have been assigned a maximum-severity […]
CISA Issues Urgent Patch Directive: Four Critical Vulnerabilities Added to Known Exploited List
In a significant move to bolster the security posture of both federal and private-sector digital infrastructure, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) has formally added four critical vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog. These additions represent a severe escalation in threat activity, as attackers are already weaponizing these flaws to gain […]
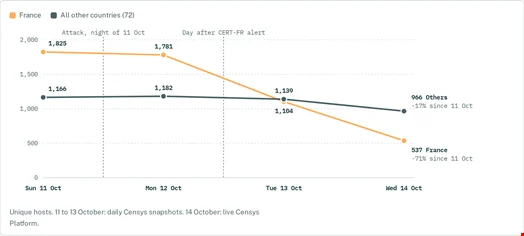
French Supermarkets Pull Refrigeration Systems Offline Following Cyber-Attack Exploiting Danfoss Vulnerabilities
PARIS — In the wake of a sophisticated cyber-incident that targeted the heartland of France’s retail and supermarket food supply chains, operators across the country have scrambled to secure their infrastructure. Rather than undertaking complex software patching cycles, facility managers have enacted an emergency operational pivot: dragging vulnerable refrigeration control systems offline entirely. Data released […]
WordPress 7.1.3 Released: Urgent Security Update Patches Seven Vulnerabilities and Four Bugs in Rapid-Fire Patch Cycle
The WordPress project has officially released WordPress 7.1.3, an emergency maintenance and security patch designed to neutralize seven distinct security vulnerabilities alongside four core bug fixes. Deployed on October 6, 2026, and coordinated by release lead Jake Spurlock, this update marks the third major security intervention for the WordPress 7.1 branch in less than three […]
Critical Security Alert: CISA Mandates Urgent Patching for Actively Exploited Windows Shell and Ivanti Vulnerabilities
In a significant escalation of cybersecurity posture, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an emergency directive to address two high-severity vulnerabilities currently being leveraged by malicious actors in the wild. The agency has formally added these flaws—a Windows Shell command injection vulnerability (CVE-2026-96951) and an authentication bypass issue in Ivanti Connect […]
Wave of Cyber Incidents Disrupts Major European Retailers, Exposing Vulnerabilities Across the Supply Chain
EUROPE — A coordinated or concurrent wave of digital disruptions has shaken the European retail sector, leaving some of the continent’s most recognizable high-street brands and multinational supermarkets grappling with network outages, offline systems, and operational paralysis. Over a tense multi-day period in mid-October, major retail conglomerates—including Ahold Delhaize, The Foschini Group (TFG), and ASOS—confirmed […]
The Rapid Exploitation Gap: A Comprehensive Analysis of the Week’s Critical Vulnerabilities and Global Cybersecurity Trends
By: Cybersecurity Intelligence Desk Published: October 12, 2026 Main Facts The cybersecurity landscape faced yet another blistering week as threat actors demonstrated an alarming ability to weaponize newly disclosed software vulnerabilities almost immediately after public publication. The most prominent incident involved a critical arbitrary file access vulnerability affecting a wide array of Atlassian Data Center […]
WordPress 7.1.1 Released: Critical Security and Maintenance Update Fixes 11 Vulnerabilities
The WordPress project has officially launched version 7.1.1, an essential maintenance and security release designed to patch a wide array of core vulnerabilities, logic flaws, and block editor bugs. This rapid-deployment update introduces a total of 17 core fixes, 19 enhancements and corrections to the Block Editor, and—most importantly—11 distinct security patches. Given the nature […]