

The WordPress project has officially launched version 7.1.1, an essential maintenance and security release designed to patch a wide array of core vulnerabilities, logic flaws, and block editor bugs. This rapid-deployment update introduces a total of 17 core fixes, 19 enhancements and corrections to the Block Editor, and—most importantly—11 distinct security patches. Given the nature […]
CISA Expands Known Exploited Vulnerabilities Catalog Amid Global Crackdown on Chinese State-Linked Espionage Infrastructure
In a significant move to fortify national security against sophisticated foreign cyber espionage, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) has formally updated its Known Exploited Vulnerabilities (KEV) catalog. The inclusion of five specific vulnerabilities—impacting ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND—marks a critical pivot in the international effort to neutralize the […]
The Weekly Cybersecurity Pulse: AI Governance, Critical Infrastructure Vulnerabilities, and the Evolution of the CISO Role
As the digital landscape becomes increasingly complex, the past week has served as a stark reminder that the intersection of artificial intelligence, legacy infrastructure, and human error remains the primary battleground for cybersecurity professionals. From the alarming exposure of European renewable energy grids to the rise of AI-generated "slop" overwhelming bug bounty programs, the industry […]
Microsoft’s Record-Breaking Patch Tuesday: 974 Vulnerabilities Shakes the Cybersecurity Industry
Main Facts: The Largest Patch Bundle in History In an unprecedented move that has sent shockwaves through the enterprise IT and cybersecurity sectors, Microsoft Corp. has issued a massive security update addressing at least 974 distinct security vulnerabilities across its Windows operating systems and associated software ecosystem. This monumental release shatters all previous corporate records, […]
DNS Vulnerabilities Exploit: Attackers Compromise Three ccTLD Registries to Obtain Unauthorized HTTPS Certificates for Google and Global Brands
Global Cybersecurity Analysis October 2023 In an alarming display of sophisticated cyber-espionage and infrastructure manipulation, malicious actors successfully compromised three country-code top-level domain (ccTLD) registries. By hijacking authoritative Domain Name System (DNS) records, the attackers managed to trick Certificate Authorities (CAs) into issuing unauthorized HTTPS certificates covering vital Google domains, as well as several other […]
ASOS Data Breach Exposes Third-Party Platform Vulnerabilities, Sparking Global Cybersecurity Scrutiny
By Global Cybersecurity & Retail Correspondent October 2023 British multinational online fashion and cosmetic retailer ASOS has confirmed that a cyberattack on October 6 compromised personal and customer account data. The breach, which unfolded via a sophisticated social engineering scheme targeting an employee’s credentials, has illuminated the pervasive and escalating risks associated with third-party software […]
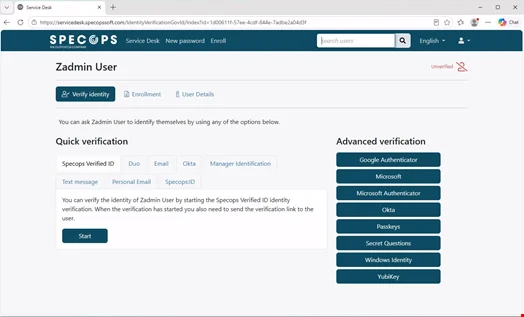
The Human Firewall is Cracking: Why AI-Driven Vishing Demands an Automated End to Service Desk Vulnerabilities
By Cybersecurity Desk Analysis Expanded and enriched reporting based on industry insights by Daniel Imber, Specops Software. For decades, the final line of defense against corporate social engineering has sat quietly at a desk, wearing a headset, waiting for the phone to ring. Service desk agents have historically served as the human firewall for internal […]
Critical Security Alert: SonicWall Addresses High-Severity Vulnerabilities in SMA 1000 Series Appliances
In an era where remote access infrastructure serves as the backbone of corporate operations, the security of these gateways has become a primary target for global threat actors. SonicWall, a leading provider of network security solutions, has issued an urgent security advisory addressing a suite of vulnerabilities within its SMA 1000 series remote access appliances. […]
Critical Security Alert: CISA Mandates Immediate Remediation for Microsoft SharePoint and MikroTik RouterOS Vulnerabilities
By Pierluigi Paganini September 25, 2026 The United States Cybersecurity and Infrastructure Security Agency (CISA) has issued a high-priority directive, mandating that all Federal Civilian Executive Branch (FCEB) agencies take immediate action to secure their infrastructure against two newly identified, actively exploited vulnerabilities. The agency has officially added CVE-2026-65660, affecting Microsoft SharePoint Server, and CVE-2026-67279, […]
Critical Security Update: WordPress 7.1.1 Released to Address 11 Vulnerabilities and 36 Core & Editor Fixes
Global Release: WordPress has officially rolled out version 7.1.1, a critical maintenance and security patch designed to fortify millions of websites worldwide. This rapid-deployment release introduces a total of 17 core bug fixes, 19 enhancements and corrections to the Block Editor, and 11 targeted security patches. The WordPress security team strongly urges all site administrators, […]