Artificial Intelligence has transitioned from a buzzword to the backbone of the modern web. From streamlining content creation to optimizing server-side performance, developers and site owners are increasingly leaning on machine learning models to reduce operational costs and improve user experiences. However, the most profound—and perhaps most volatile—impact of AI is currently unfolding in the realm of cybersecurity.
As AI models become more adept at parsing complex codebases, they are redefining how we identify, report, and patch security vulnerabilities. While this technological leap promises a safer internet, it also introduces a "security paradox": the same tools used to fortify our digital infrastructure are providing malicious actors with unprecedented capabilities to compromise it. For web professionals, the brave new world of AI-assisted security is not just an opportunity; it is an existential challenge.
The Evolution of AI in Security Research
The integration of AI into security workflows began as an experimental endeavor but has quickly become a standard practice. Historically, security research was a laborious, manual process. Expert auditors would comb through thousands of lines of code, looking for deviations from secure programming patterns.
Today, AI-driven scanners have fundamentally altered this timeline. By training Large Language Models (LLMs) on extensive libraries of documentation and known vulnerabilities in languages like PHP and JavaScript, developers have created "virtual researchers" that can analyze entire repositories in hours, not weeks.
Chronology of the AI Shift
- The Early Adoption Phase: Initial AI tools focused on simple pattern matching, flagging basic coding errors or deprecated functions.
- The Predictive Era: Mid-2020s models began identifying logical flaws. Unlike static analysis tools, these models started recognizing how disparate code snippets could interact to form a vulnerability.
- The "Protect the Shire" Milestone: The WordPress community’s "Protect the Shire" initiative represents a turning point where AI was formalized as a gatekeeping mechanism to scan plugins for security holes before they hit the public repository.
- The Current State: We are now in a period of exponential discovery, where the sheer volume of vulnerability reports is testing the limits of human incident response teams.
AI Makes Connections Humans Can’t
The true power of AI in cybersecurity lies in its ability to perceive patterns that are invisible to the human eye. In complex software ecosystems, a single file might appear perfectly secure when audited in isolation. However, an AI can trace the flow of data across multiple, seemingly unrelated modules, identifying "choke points" where a malicious payload could trigger a chain reaction.
This detective work has already yielded significant results. Recent security audits have uncovered backdoors that had remained hidden for over a decade. These vulnerabilities were not "obvious" flaws; they were sophisticated logical oversights that required a holistic view of the application architecture—a view that LLMs provide with remarkable speed.

Battling Information Overload: The Double-Edged Sword
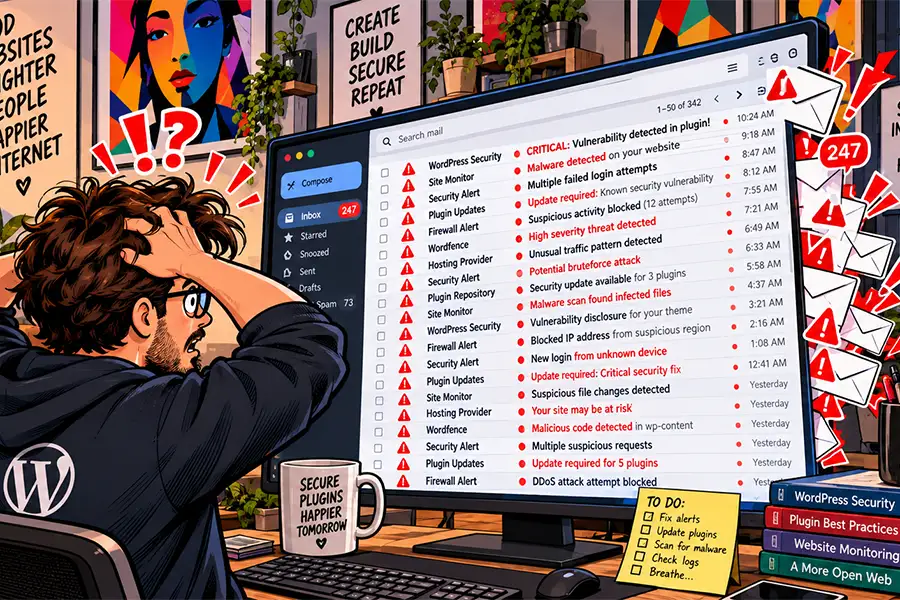
While the ability to identify vulnerabilities is a victory for security, it has created a secondary crisis: data saturation. Bug bounty programs that previously managed a manageable trickle of reports are now overwhelmed by hundreds of submissions per month.
Supporting Data and Observations
The sheer volume of reports creates a "noise" problem. Security teams are now forced to triage an unprecedented number of warnings. This creates several critical dilemmas:
- Prioritization Fatigue: Not all vulnerabilities are created equal. Some represent critical entry points, while others are edge cases that are statistically unlikely to be exploited.
- The "Doomsday" Marketing Cycle: The increase in discovered flaws has been weaponized by some security vendors, leading to a climate of fear where every minor patch is marketed as a critical emergency to sell defensive tools.
- The Public Exposure Trap: Once a vulnerability is public, the clock starts ticking. Attackers—who are also using AI to generate exploit code—can move faster than human developers can deploy patches.
Official Responses and Industry Shifts
Organizations like the WordPress Foundation and major hosting providers are acknowledging that the current model of security management is unsustainable for the average freelancer or agency. The traditional approach—where developers manually monitor, test, and patch individual sites—is failing in the face of this AI-generated deluge.
Industry leaders are increasingly calling for a "Security-as-a-Service" evolution. Rather than leaving the burden of patching on the site owner, there is a push to shift responsibility toward the infrastructure level.
The Shift Toward Infrastructure-Level Defense
- Automated Hosting Intelligence: Web hosts are beginning to implement AI-driven firewalls that can detect and block exploit attempts in real-time before they reach the application layer.
- CDN-Level Mitigation: Services like Cloudflare and Akamai are positioning themselves as the first line of defense, using machine learning to identify traffic patterns associated with specific, newly discovered vulnerabilities and neutralizing them at the edge.
- The Move Toward "Smart" Updates: There is a growing movement toward intelligent, automated patching systems that test updates in a sandbox environment before automatically pushing them to production sites, reducing the risk of site-breaking updates.
Implications for Web Professionals
For freelancers, agencies, and web developers, the rise of AI in security creates a significant pivot point in professional responsibilities. We are moving away from the era of "set it and forget it" maintenance.
Will AI Make Our Jobs Easier?
In the short term, AI tools will likely make the job of a developer more difficult. The expectation to keep a site secure against an ever-increasing volume of AI-discovered threats creates a constant state of anxiety. However, in the long term, if integrated correctly, these tools could automate the most tedious parts of maintenance.

The Risk of Backfire
The greatest danger is the reliance on automated systems that we do not fully understand. If a developer relies solely on an AI-based security plugin without maintaining a foundational understanding of secure coding practices, they become vulnerable to "blind spots" in the AI’s logic. If the AI is trained on a dataset that contains its own biases or gaps, it may provide a false sense of security while leaving the site open to novel, non-pattern-based attacks.
Conclusion: A Call for Smarter Management
The explosion of security discoveries driven by AI is a double-edged sword that the web development industry is only just beginning to grasp. We have entered an era where the speed of threat identification is outstripping the human capacity to respond.
To survive this "brave new world," we must move beyond individual, manual efforts. We need a more unified, ecosystem-wide approach to security that leverages AI to do the heavy lifting of patch management and threat detection at the infrastructure level.
Freelancers and agencies can no longer afford to act as islands of security. The solution lies in better partnerships with hosting providers, the adoption of edge-based protection, and a critical, informed engagement with the tools that claim to make our sites safer. The robots are indeed here to help—but it is up to us to ensure they are helping us build a fortress, not just identifying the cracks in our walls.