










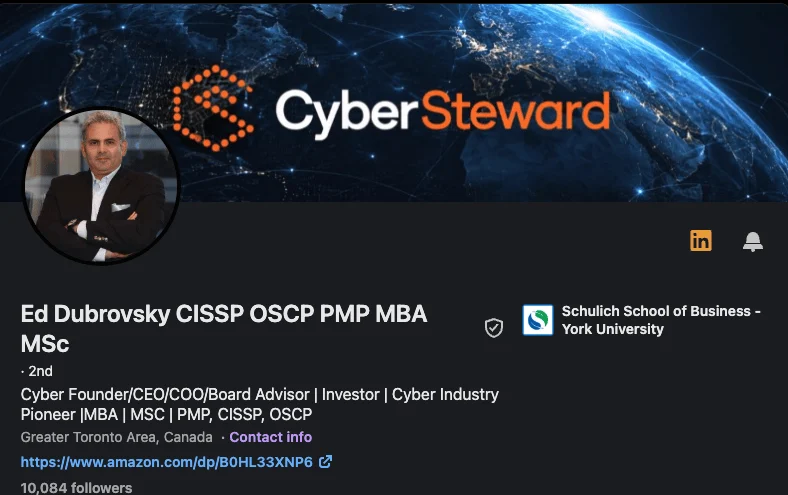
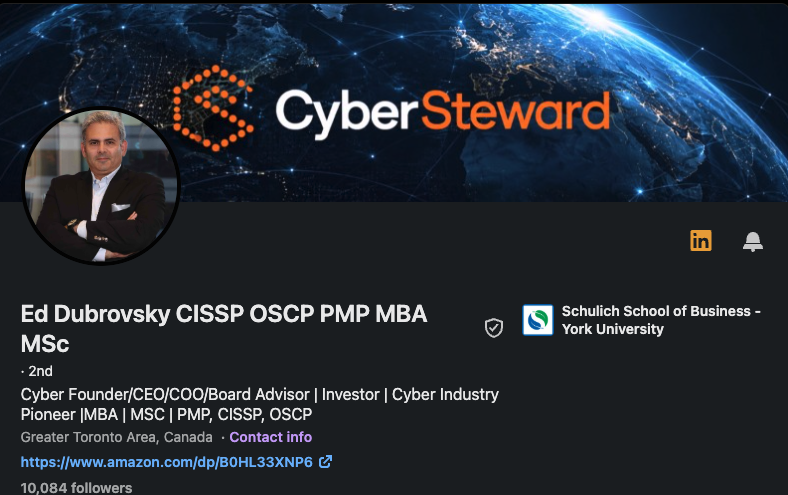
In a development that has sent shockwaves through the cybersecurity and cyber-insurance sectors, a prominent Canadian ransomware negotiator was taken into federal custody on October 8, 2026. The arrest, executed in Philadelphia, represents a significant escalation in the FBI’s aggressive, multi-jurisdictional pursuit of the notorious hacking collective known as "ShinyHunters."
While federal court documents remain largely sealed, the arrest of Edward Dubrovsky—a recognized figure in the field of ransomware mediation—raises profound questions about the thin line between professional threat negotiation and potential criminal complicity. As the FBI continues to dismantle the infrastructure of the ShinyHunters group, the arrest of an industry insider suggests that the Bureau’s net is tightening not just around hackers, but potentially around those who facilitate the financial resolution of cyber-attacks.
Main Facts: The Arrest of Edward Dubrovsky
The apprehension of Edward Dubrovsky occurred in the midst of the Cyber Risk Summit, a high-profile industry gathering held at the Loews Philadelphia Hotel. Sources indicate that Dubrovsky, a veteran in the field of cyber-extortion response, was in the city to attend the event alongside representatives from his firm, CyberSteward.
Court filings in the Eastern District of Pennsylvania initially linked a defendant named "Edward Dobrovsky" (with variations in spelling) to charges of conspiracy to "threaten to impair the confidentiality of information with intent to extort money" and "interference with commerce by threats." While the primary criminal complaint remains under seal—leaving the specific nature of his alleged actions to speculation—the charges suggest that federal prosecutors believe his professional activities crossed the threshold into criminal enterprise.
Dubrovsky is a well-known entity in the cybersecurity world. Formerly associated with the Canadian security firm Cypfer, he transitioned to CyberSteward, a company that specializes in threat actor engagement and complex ransomware negotiations. He has previously authored literature on responding to cyber-extortion, positioning himself as a subject matter expert in navigating the volatile landscape of digital ransom payments. His arrest, therefore, is not merely the capture of an alleged criminal, but a strike at the heart of the ecosystem that manages the fallout of global ransomware incidents.
Chronology: A Global Manhunt Intensifies
The arrest of Dubrovsky is the third such operation in a series of targeted actions aimed at neutralizing ShinyHunters within a single month. The group has become a primary target for the FBI following their brazen claim last month that they had breached an FBI-affiliated system to steal sensitive information on federal employees.
A Timeline of Recent Escalations:
- Mid-September 2026: FBI investigations into ShinyHunters gain momentum as international partners assist in tracking key nodes of the group’s operations.
- September 15, 2026: A suspected member of the ShinyHunters collective is apprehended in the Netherlands, marking the first major success in this specific cycle of arrests.
- September 28, 2026: A second, high-level member of the group is detained in Jordan. Reports suggest this individual is currently cooperating with the FBI, providing critical intelligence on the group’s hierarchy and methodologies.
- October 5–7, 2026: The Cyber Risk Summit takes place in Philadelphia. Dubrovsky is present, presumably to network and share insights on his field.
- October 8, 2026: Federal agents execute an arrest warrant for Edward Dubrovsky in Philadelphia.
- October 9, 2026: The case is officially transferred to the Eastern District of Texas, a jurisdiction where the FBI’s centralized investigation into ShinyHunters is headquartered. FBI Director Kash Patel confirms the arrest via public channels, framing it as part of a broader, ongoing campaign to dismantle the syndicate.
Supporting Data: The Shadow of ShinyHunters
ShinyHunters has established itself as one of the most prolific and disruptive threat actors in the modern digital age. The group’s modus operandi typically involves the theft of massive databases followed by high-stakes extortion. However, their recent pivot toward targeting law enforcement agencies—specifically the FBI—signaled a tactical shift that invited unprecedented federal scrutiny.
According to the FBI, the recent breach of an FBI-affiliated platform, which the Bureau attributed to a third-party vendor’s failure to patch Oracle PeopleSoft software, resulted in the exposure of personnel data. This act of "cyber-defiance" transformed the group from a criminal nuisance into a top-tier national security priority.
The financial scale of their operation is equally staggering. Federal authorities estimate that ShinyHunters has extorted more than $70 million in ransom payments over the course of 2026 alone. This massive influx of capital has fueled the group’s expansion, allowing them to recruit sophisticated talent and refine their exploitation techniques. The involvement of professional negotiators, such as the defendant, has long been a subject of debate in the intelligence community, with some fearing that such services inadvertently subsidize the very criminal enterprises they are hired to neutralize.
Official Responses and Legal Status
The response from the FBI has been measured but firm. Director Kash Patel’s public acknowledgment of the arrest serves as a warning to both the hackers and the "service providers" that orbit them. In his statement, Patel emphasized that the FBI’s agents in the field are actively dismantling the network, piece by piece.
However, the legal landscape surrounding Dubrovsky remains murky. The discrepancy in the spelling of his name in court documents—appearing as both "Dobrovsky" and "Dobrosky"—is indicative of the rapid, fluid nature of the investigation. Furthermore, the transfer of the case to the Eastern District of Texas suggests that prosecutors in Pennsylvania were acting as the initial point of contact for the arrest, but that the broader, more complex indictment is being handled by a team specialized in large-scale cyber-conspiracy cases.
As of this writing, neither the FBI nor the U.S. Attorney’s Office for the Eastern District of Pennsylvania has provided further clarification regarding the specific evidentiary basis for the charges. Attempts by international media outlets to reach legal counsel for the defendant or representatives from CyberSteward have remained unsuccessful, as the firm has maintained a wall of silence regarding the incident.
Implications: The Future of Ransomware Negotiation
The arrest of a professional ransomware negotiator poses a significant threat to the status quo of incident response. For years, companies have relied on firms like CyberSteward to navigate the "gray zone" of cybersecurity—hiring experts to talk down hackers, verify decryption keys, and manage the delicate, often expensive process of paying ransoms to ensure business continuity.
If the FBI’s case against Dubrovsky succeeds, it could set a dangerous precedent for the industry. Many cybersecurity professionals argue that their role is essential to mitigating harm for victimized organizations. Conversely, federal prosecutors may be attempting to establish that providing professional "mediation" services to known criminal entities violates anti-extortion and anti-money laundering statutes.
Key Considerations for the Industry:
- Legal Jeopardy: The case may force negotiation firms to implement stricter "Know Your Customer" (KYC) protocols to ensure they are not inadvertently facilitating the criminal goals of threat actors.
- Regulatory Scrutiny: We may see a push for formal oversight or licensing of cyber-negotiators to differentiate between legitimate security consultants and those who may be overstepping the legal bounds.
- The "Chilling Effect": If negotiation becomes a high-risk legal activity, companies may find themselves with fewer resources to respond to ransomware attacks, potentially leading to higher rates of data exposure or prolonged downtime for critical infrastructure.
As the investigation moves to the Eastern District of Texas, the cybersecurity world remains in a state of high tension. The case of Edward Dubrovsky is likely to become a landmark trial, defining the boundaries of what is legally permissible in the war against digital extortion. For now, the arrest serves as a stark reminder: in the digital landscape, the line between the white-hat advisor and the black-hat accomplice is becoming increasingly difficult to discern—and federal authorities are no longer willing to give the benefit of the doubt.



