

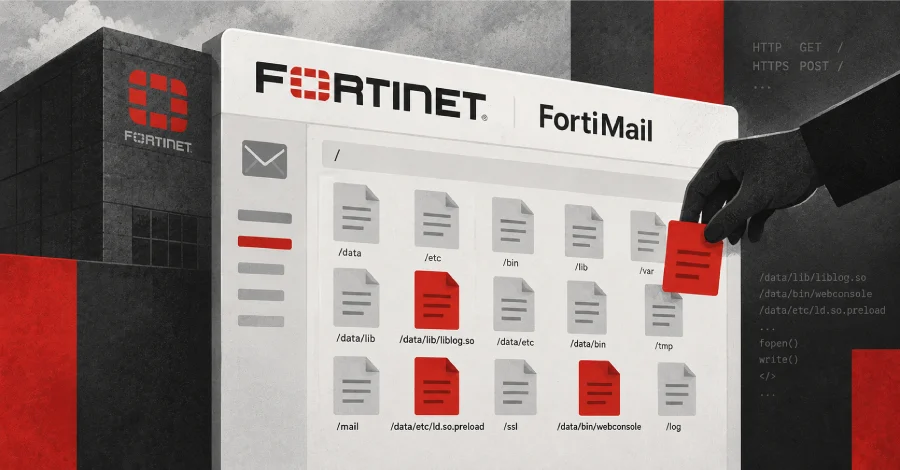
By Ravie Lakshmanan | October 02, 2026 Vulnerability / Enterprise Security Main Facts The United States Cybersecurity and Infrastructure Security Agency (CISA) has officially added a critical security vulnerability impacting Fortinet’s FortiMail secure email gateway to its heavily watched Known Exploited Vulnerabilities (KEV) catalog. The inclusion follows mounting intelligence and direct telemetry confirming that threat […]
Critical Security Alert: CISA Mandates Immediate Remediation for Microsoft SharePoint and MikroTik RouterOS Vulnerabilities
By Pierluigi Paganini September 25, 2026 The United States Cybersecurity and Infrastructure Security Agency (CISA) has issued a high-priority directive, mandating that all Federal Civilian Executive Branch (FCEB) agencies take immediate action to secure their infrastructure against two newly identified, actively exploited vulnerabilities. The agency has officially added CVE-2026-65660, affecting Microsoft SharePoint Server, and CVE-2026-67279, […]

CISA Overhauls Insider Threat Mitigation Guide to Address AI, Remote Work, and Evolving Workplace Dynamics
WASHINGTON — In response to a rapidly shifting corporate and operational landscape, the Cybersecurity and Infrastructure Security Agency (CISA) has officially released a comprehensive, updated version of its foundational Insider Threat Mitigation Guide. Published on September 9, the revised framework incorporates fresh case studies, contemporary empirical data, and targeted guidance to help organizations navigate the […]
Lessons in Transparency: A Postmortem of CISA’s Six-Month Credential Leak
In an era where the Cybersecurity and Infrastructure Security Agency (CISA) stands as the vanguard of American digital defense, the irony of a massive internal data leak originating from within its own ranks has sent shockwaves through the cybersecurity community. For six months, hundreds of sensitive credentials—including high-level Amazon AWS GovCloud administrative keys and plaintext […]
CISA: Patch actively exploited SolarWinds Serv-U DoS vulnerability (CVE-2026-28318)
A vulnerability (CVE-2026-28318) that can be exploited to crash SolarWinds Serv-U file transfer servers is being leveraged by attackers in the wild, the US Cybersecurity and Infrastructure Security Agency (CISA) confirmed on Friday. The agency has ordered US federal civilian agencies to address it by June 19, 2026, either by implementing a patch or implementing […]