










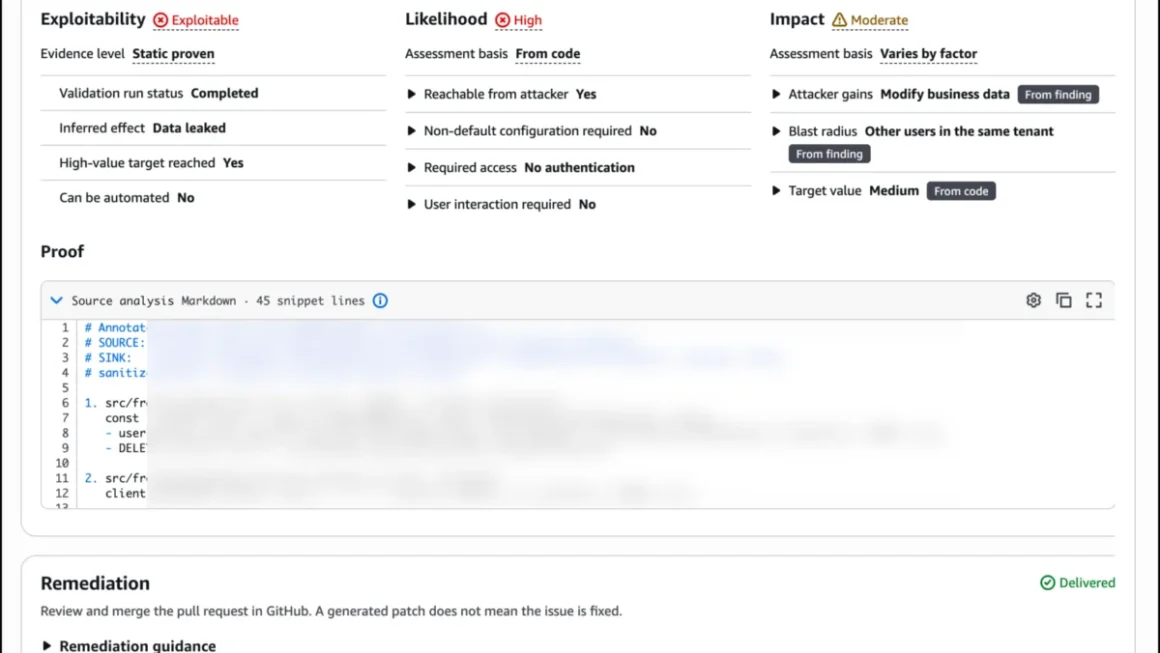
SEATTLE — In an era where malicious actors leverage frontier artificial intelligence models to weaponize vulnerability disclosures within minutes, enterprise security teams face an unprecedented deluge of alerts. Modern application scanners frequently flood security operations centers with thousands of findings daily—many of which prove unreachable, entirely unexploitable, or already neutralized by existing runtime controls. Addressing […]
Headline
Tag: continuum
Back To Top