










In an increasingly volatile cybersecurity landscape, Google has once again been forced to move on the defensive. This week, the technology giant released a critical stable channel update for its ubiquitous Chrome browser, addressing a total of 11 security vulnerabilities. Among these fixes is a high-severity zero-day flaw that has already been confirmed to be […]
Apple Issues Urgent Security Patch for Active Zero-Day Exploits: What Users Need to Know
In a critical security alert issued this week, Apple has urged all users of macOS, iPhone, and iPad to immediately update their devices. The software patches, released for iOS 15.6.1 and macOS Monterey 12.5.1, address two high-severity zero-day vulnerabilities that are currently being actively exploited in the wild. These flaws grant attackers the ability to […]
The Patch Apocalypse: Navigating the Record-Breaking Vulnerability Landscape of Late 2026
The cybersecurity landscape has entered a period of unprecedented volatility. As we traverse the fourth month of what industry analysts have dubbed the "Patch Apocalypse," the sheer volume of CVEs (Common Vulnerabilities and Exposures) being reported has reached a staggering, all-time high. For IT administrators and security professionals, the routine of Patch Tuesday—once a manageable […]
WordPress 7.1.2 Released to Patch Critical Remote Code Execution Vulnerability Affecting Global Installations
The open-source content management system powering over 40% of the web has issued an urgent security update. Version 7.1.2 fixes a critical-severity vulnerability that could allow unauthenticated attackers to trigger Local File Inclusion (LFI) and potentially achieve Remote Code Execution (RCE) under specific server configurations. Main Facts The WordPress security team has officially announced the […]
Critical CSRF Vulnerability in Elementor Plugin Threatens Millions of WordPress Sites: Immediate Patch Issued
By Cybersecurity Desk Published: October 2023 The web security community has recently raised alarms regarding a severe security flaw discovered in Elementor, one of the most ubiquitous visual page builder plugins for WordPress. A high-severity Cross-Site Request Forgery (CSRF) vulnerability, affecting versions 4.3.0 and 4.3.1, has exposed millions of websites to potential full-site takeover risks. […]
Microsoft’s Record-Breaking Patch Tuesday: 974 Vulnerabilities Shakes the Cybersecurity Industry
Main Facts: The Largest Patch Bundle in History In an unprecedented move that has sent shockwaves through the enterprise IT and cybersecurity sectors, Microsoft Corp. has issued a massive security update addressing at least 974 distinct security vulnerabilities across its Windows operating systems and associated software ecosystem. This monumental release shatters all previous corporate records, […]
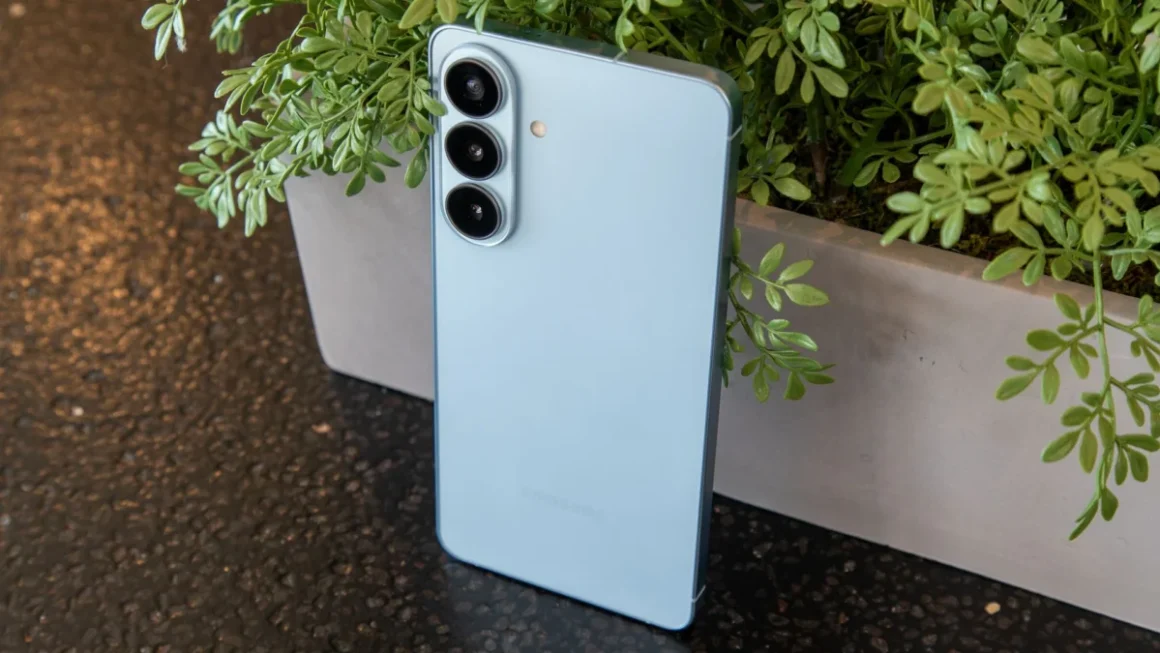
Samsung Deploys Critical October 2026 Security Patch for Galaxy S26 Series: What You Need to Know
By Android Central Tech Desk Published: October 2026 Samsung has officially begun its global rollout of the October 2026 security patch, prioritizing its latest flagship generation, the Galaxy S26 series. Following hard on the heels of the major Android 17-based One UI 9 deployment, this latest firmware update aims to fortify Samsung’s premier devices against […]
WordPress 7.1.3 Emergency Release: A Deep Dive into Seven Critical Security Fixes and the Rapid Patch Cycle
The WordPress project team has officially released WordPress 7.1.3, an emergency maintenance and security update deployed on October 6, 2026. This vital release addresses a total of eleven issues—comprising seven security vulnerabilities and four general maintenance bugs. Coming on the heels of an exceptionally turbulent patch cycle, the core development team is strongly advising all […]

The New Frontier of Digital Defense: Navigating the Era of Autonomous AI Threats and Accelerated Patch Cycles
Date: September 30, 2026 Report by: Cybersecurity Editorial Desk Expert Commentary: Tony Anscombe, ESET Chief Security Evangelist As the digital landscape closes the books on September 2026, the cybersecurity community finds itself grappling with a paradigm shift. The convergence of two distinct phenomena—the emergence of autonomous AI-driven cyberattacks and an unprecedented surge in software vulnerability […]
The Patch Tuesday Paradox: Microsoft’s September Updates Reveal the Fragility of Modern Security Deployment
The age-old mantra of IT departments everywhere—"patch early and often"—has long served as the cornerstone of cybersecurity hygiene. However, the September 2026 Patch Tuesday cycle has served as a sobering reminder of the "Patch Tuesday Paradox": the urgent need to address critical vulnerabilities often clashes with the operational reality of introducing new, disruptive bugs into […]