










In a chilling revelation that highlights the profound vulnerabilities within the global consumer electronics supply chain, security researchers at Bitdefender have uncovered a sophisticated, long-running malware campaign dubbed "Midnight Mimosa." This campaign has successfully compromised thousands of low-cost Android smartphones by embedding malicious code directly into the device firmware before they even reach the consumer. […]
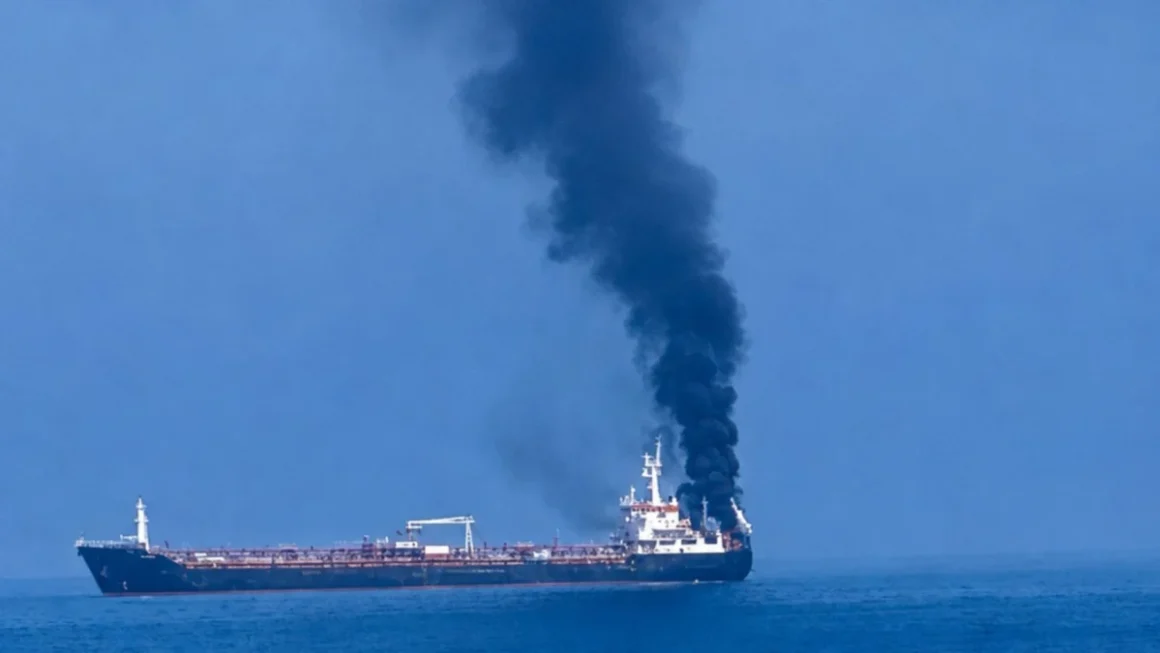
Maritime Crossroads in Crisis: 11 Indian Seafarers Dead as West Asia Conflict Strangles Global Supply Chains
New Delhi — The cascading fallout of geopolitical instability in West Asia has exacted a heavy human toll on India’s maritime workforce. Ministry of Ports, Shipping and Waterways (MoPSW) Secretary Vijay Kumar announced on Monday that 11 Indian seafarers have lost their lives since the inception of the regional conflict. The announcement came during a […]
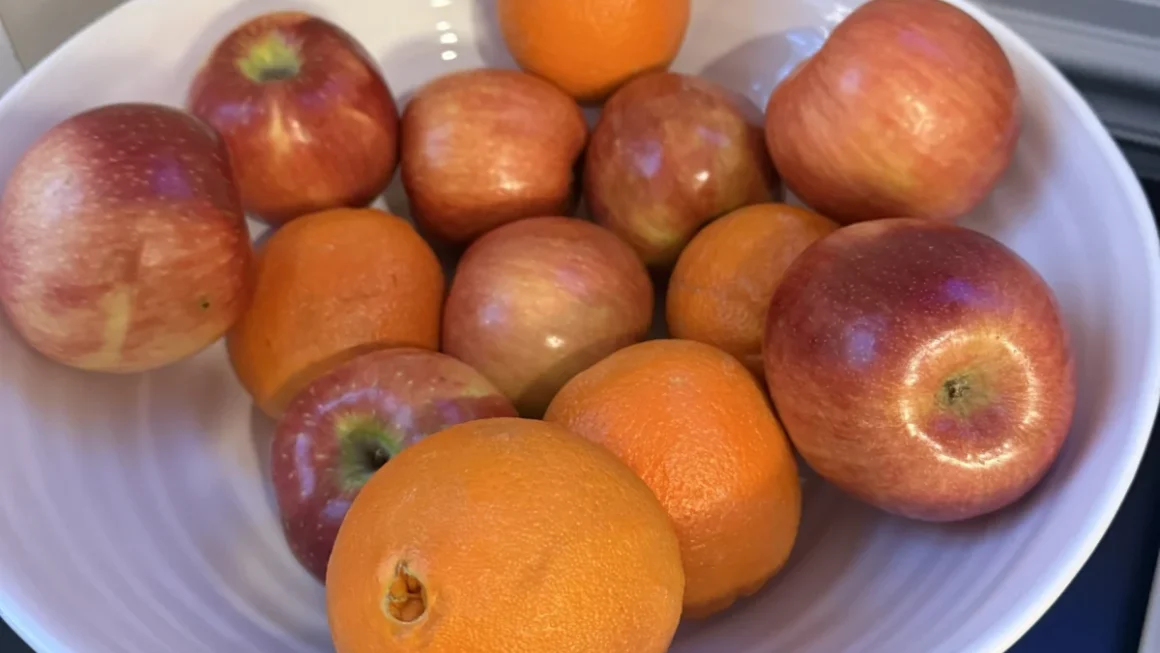
The Geography of Compromise: What a Hotel Gym Apple Reveals About Modern Supply Chains and Institutional Inertia
CAPE COD, MASSACHUSETTS — October is the undisputed crown jewel of the New England calendar. Across the rolling hills of Massachusetts, Vermont, New Hampshire, and Maine, the crisp autumn air carries the sharp, sweet aroma of heirloom apple varieties freshly pulled from local branches—McIntosh, Honeycrisp, Cortland, and Macoun. Agricultural authorities and culinary tourists alike routinely […]
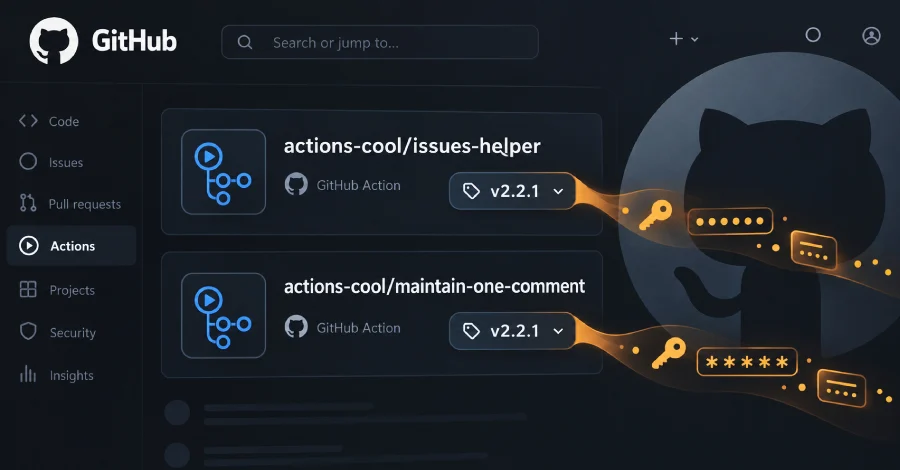
Ghost in the Pipeline: The Re-emergence of the "Mini Shai-Hulud" Supply Chain Attack on GitHub Actions
By Global Cybersecurity Desk Published: September 25, 2026 Executive Summary In a startling display of persistent software supply chain vulnerabilities, two popular GitHub Actions repositories associated with the infamous "Mini Shai-Hulud" threat campaign were briefly brought back to life this September, months after being flagged and disabled for malicious activity. Security researchers at software supply […]