

In a rare and sophisticated intervention that sits at the intersection of ethical hacking and digital public health, cybersecurity researchers at Eye Security have successfully neutralized a massive security vulnerability embedded within an abandoned fork of the popular, yet controversial, BitTorrent streaming application, Popcorn Time.
The vulnerability, tracked as CVE-2026-30612, affected the "Time4Popcorn" fork, leaving an estimated 3.35 million computers—ranging from residential home setups to sensitive corporate and military environments—wide open to Remote Code Execution (RCE) attacks. Had malicious actors discovered the flaw first, they would have possessed the keys to a global botnet of unprecedented scale, capable of deploying ransomware, surveillance tools, or destructive payloads with SYSTEM-level or root-level privileges.
The Anatomy of a Digital Time Bomb
The crisis centered on a fundamental failure in how the Time4Popcorn application handled software updates. The client was programmed to poll a specific, abandoned domain—popcorntimeupd.xyz—for update packages. Crucially, the application performed these checks over unencrypted HTTP and, more dangerously, failed to verify the digital signatures of the files it downloaded.
By essentially operating on the "honor system," the application was primed to execute any file sent from the domain as if it were a legitimate update from the developers. Because the domain had been allowed to expire, it became a prime target for "domain squatting" or acquisition.
When researchers at Eye Security acquired the domain, they realized the extent of the risk. Because the application was essentially "calling home" to an infrastructure they now controlled, they could effectively push arbitrary code to every single active instance of the software globally. The potential for a catastrophic supply-chain attack was not merely theoretical; it was an active, ticking clock.
Chronology of an Intervention
The operation to secure these devices was neither quick nor simple. It required a methodical, legal, and technical approach to ensure that the "remediation" did not itself violate the privacy or security of the users it was intended to protect.
Phase 1: Discovery (Late 2025)
Eye Security researchers stumbled upon the vulnerability during routine infrastructure analysis. Upon registering the abandoned domain, they were met with a staggering flood of traffic. Telemetry data indicated that approximately 3 million Windows clients and 350,000 macOS clients were actively polling the server, despite the application having been largely abandoned by its original maintainers.
Phase 2: Strategic Remediation (November 2025 – March 2026)
Rather than simply shutting down the domain—which would have left the millions of dormant installations still vulnerable to whoever might register the domain next—the team opted to use the vulnerable mechanism against itself. They engineered a benign "remediation payload."

This payload was designed to perform one task: disable the auto-updater service permanently. To ensure the safety of the users, the researchers programmed the script to perform no data exfiltration, no file deletion, and no system modification beyond the specific task of killing the updater.
The process faced significant hurdles. During testing, the researchers discovered that modern Antivirus (AV) and Endpoint Detection and Response (EDR) solutions flagged their remediation tool as malicious. They were forced to iterate on the payload, refining its behavior to avoid being blocked by the very security products meant to protect the users.
Phase 3: The Quiet Shutdown (March 2026)
By March 1, 2026, the success of the operation was evident. Requests to the update domain had plummeted by 98%. With the risk significantly mitigated, Eye Security transferred the ownership of the domains to The Shadowserver Foundation, a non-profit organization dedicated to improving the security of the internet.
Supporting Data: A Global Footprint
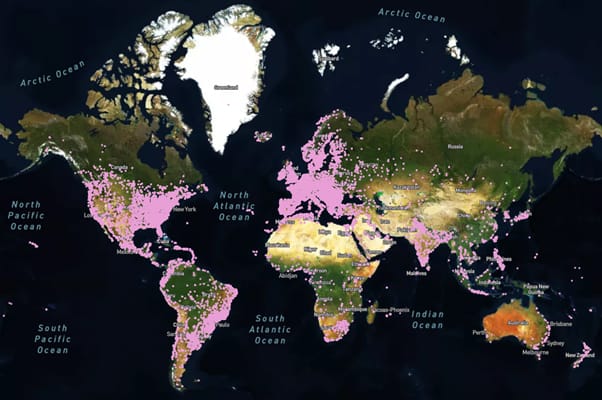
The reach of the Time4Popcorn application was far wider than the researchers initially anticipated. By mapping the incoming connections, Eye Security visualized a global footprint that traversed every continent.
Crucially, the telemetry revealed that these connections were not coming from a concentrated cluster of users, but were distributed across:
- Residential ISPs: Representing the bulk of home users who had downloaded the app years prior and likely forgotten it.
- Corporate Networks: Suggesting that many users had installed the software on work machines, potentially bypassing organizational security policies.
- Government and Military Networks: Perhaps the most concerning discovery, showing that even high-security environments were not immune to the "install and forget" culture that plagues modern desktop software.
The researchers noted a recurring theme: most of these devices were not being used for streaming. The software was effectively "dead weight" on millions of hard drives, yet it remained an active, dangerous entry point for any threat actor savvy enough to point a DNS record toward it.
Official Responses and Ethical Implications
The incident has sparked a broader conversation regarding the "right to repair" software and the responsibilities of developers when abandoning projects.
Eye Security’s actions have been widely praised by the security community as a "white-hat" operation of the highest order. However, the legal framework surrounding such interventions remains murky. By executing code on users’ machines—even with benign intent—the researchers technically bypassed the standard boundaries of system ownership.
"If we were able to send an update, we could potentially get code execution on millions of systems," the researchers stated in their report. "The impact would be severe if this were to fall into the wrong hands. We chose to act because the risk to the global ecosystem was too high to ignore."
The Shadowserver Foundation, now the steward of the infrastructure, has noted that while this specific vector is closed, the project serves as a stark reminder of the "orphaned software" problem. When software projects die, the infrastructure they rely on often remains a dormant trap waiting for the next opportunistic attacker.
The Lingering Danger: Why the Risk Remains
Despite the success of the remediation, the researchers emphasize that users of the Time4Popcorn app are not entirely out of the woods. The "cleanup" operation was limited in scope, and several critical vulnerabilities persist:
- The Android Problem: The mobile version of the application does not function in the same way as the desktop clients. Because Android updates typically require explicit user interaction, the researchers were unable to push the remediation payload to mobile devices. Users of the Android version remain at risk.
- Architectural Rot: Beyond the updater, the Time4Popcorn client is built on a heavily outdated version of the Chromium engine (circa 2014). This engine lacks modern sandbox protections, meaning that even if the updater is disabled, the app itself remains a playground for exploit developers. Any website or malicious file opened within the app could potentially compromise the entire host operating system.
- The "Forgotten" Factor: The greatest security risk remains the users themselves. Because the software was installed and "forgotten," many users may not even realize it is still sitting on their systems, consuming resources and acting as a hidden, dormant vulnerability.
Recommendations for Users
The consensus among cybersecurity professionals is clear: there is no patch that can secure an abandoned, architecturally obsolete application.
If you or your organization have "Time4Popcorn" or any derivative of the original "Popcorn Time" software installed, the only effective security measure is total removal.
- Audit your systems: Use administrative tools to scan for the existence of the application.
- Uninstall immediately: Do not rely on the application’s built-in uninstaller if you suspect it may be compromised. Use a reputable third-party uninstaller or perform a manual cleanup of the application’s directory and associated registry keys/plists.
- Update your threat modeling: Treat the presence of abandoned software as a high-risk security event. Organizations should implement policies that restrict the installation of unauthorized streaming software, particularly those that rely on peer-to-peer (P2P) infrastructure.
The "Popcorn Time" incident of 2026 serves as a definitive case study in the dangers of the "shadow IT" landscape. While Eye Security managed to avert a potential global cyber disaster, the episode highlights a fragile reality: the security of our digital world often relies on the benevolent actions of a few, while millions of devices remain one expired domain registration away from total compromise.